Confluence v6.15.10
Original user directory structure
- Delegated LDAP Authentication - Microsoft Active Directory
- Confluence Internal directory
New user directory structure
- Active Directory Server - Microsoft Active Directory (Read Only, with Local Groups)
- Delegated LDAP Authentication - Microsoft Active Directory
- Confluence Internal directory
All user directories are active
- Reason for change.
- use MS groups for SPACE permisions, previously manually adding users to internal groups
- sync selected groups with MS AD
- restrict number of MS AD users who will have access (license limits)
- Tried this process using Delegated LDAP Auth
- AD groups not added until a user logged in. Therefore could not manage space access efficiently.
After synching with MS AD using (3) all internal groups are not visible
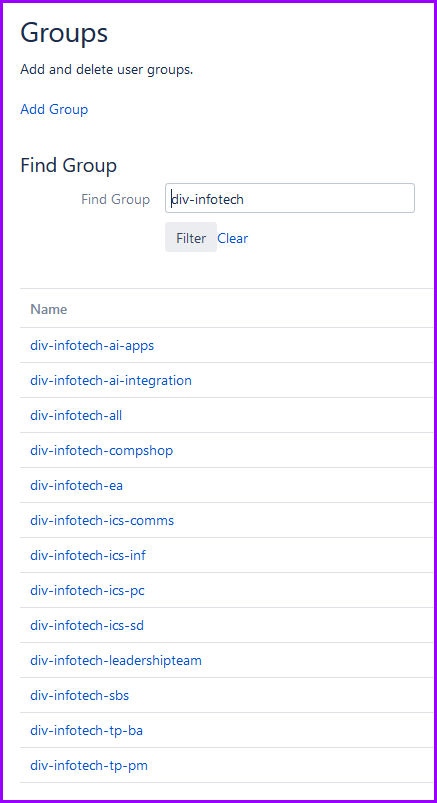
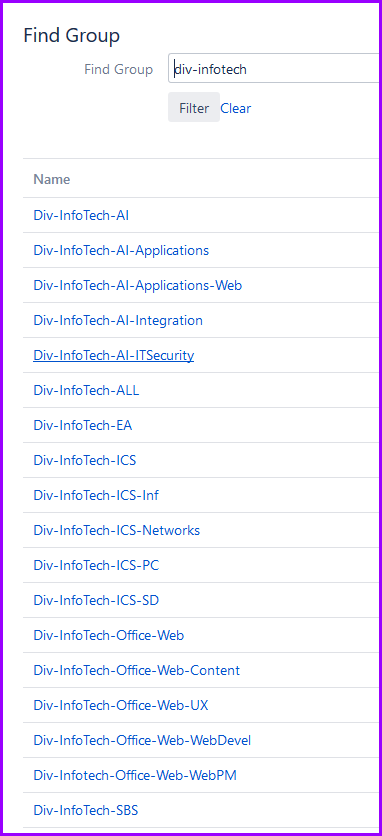
If I try to recreate the internal group
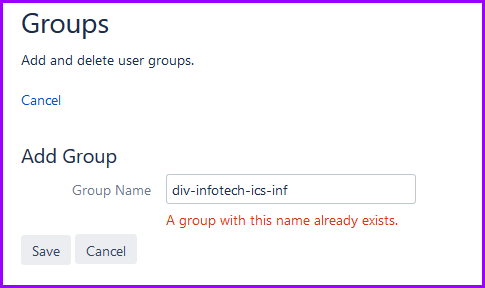
Is there a way to reactivate these groups since all the space permissions is currently based on these groups.
regards
Gary

