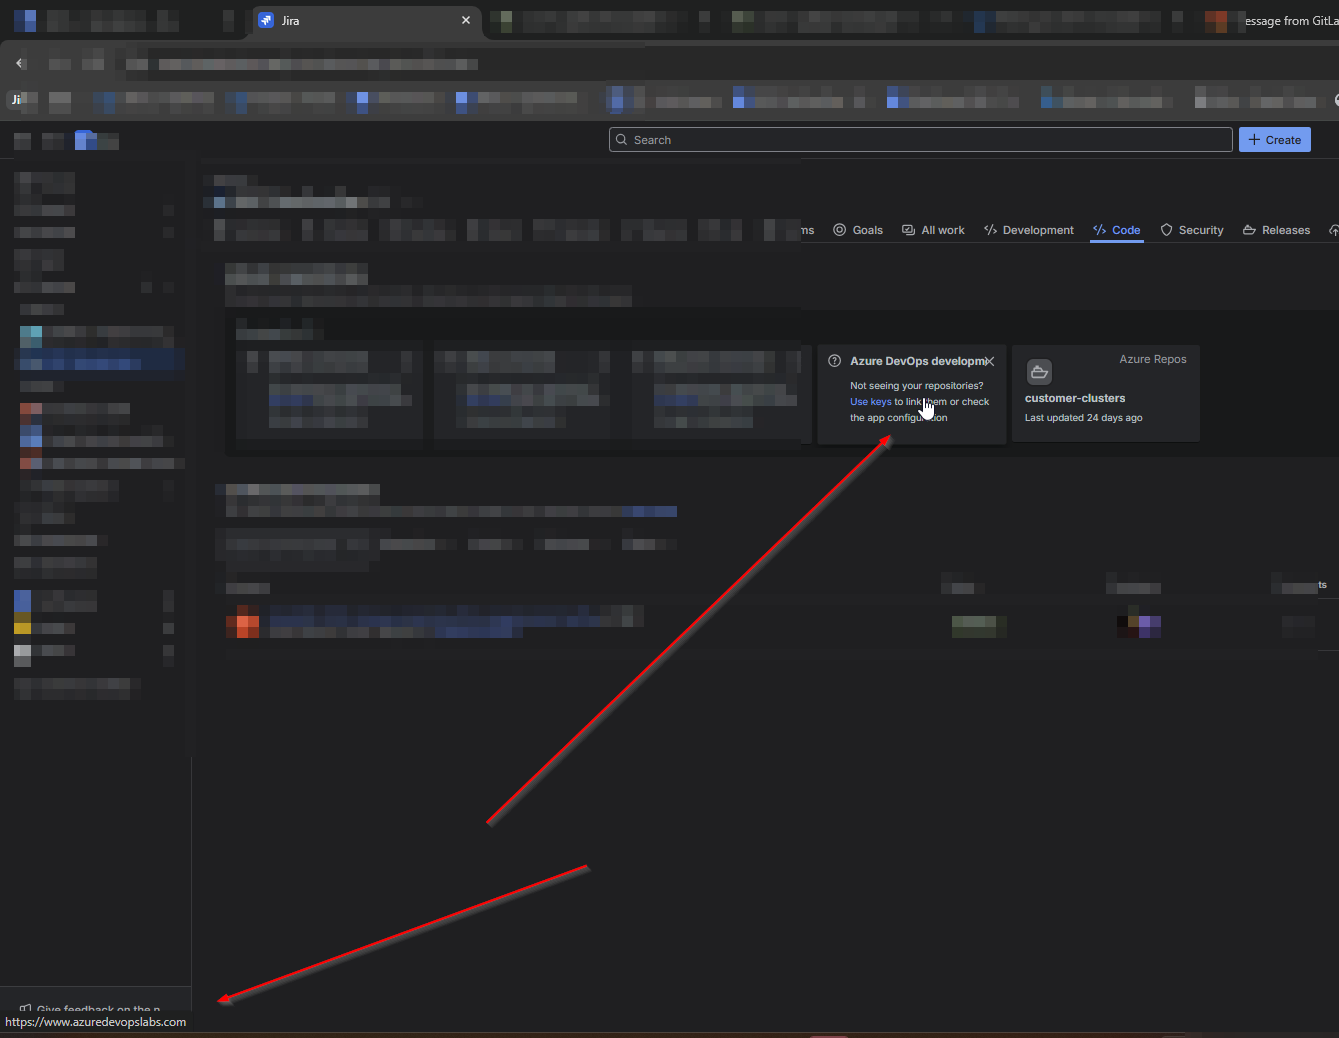
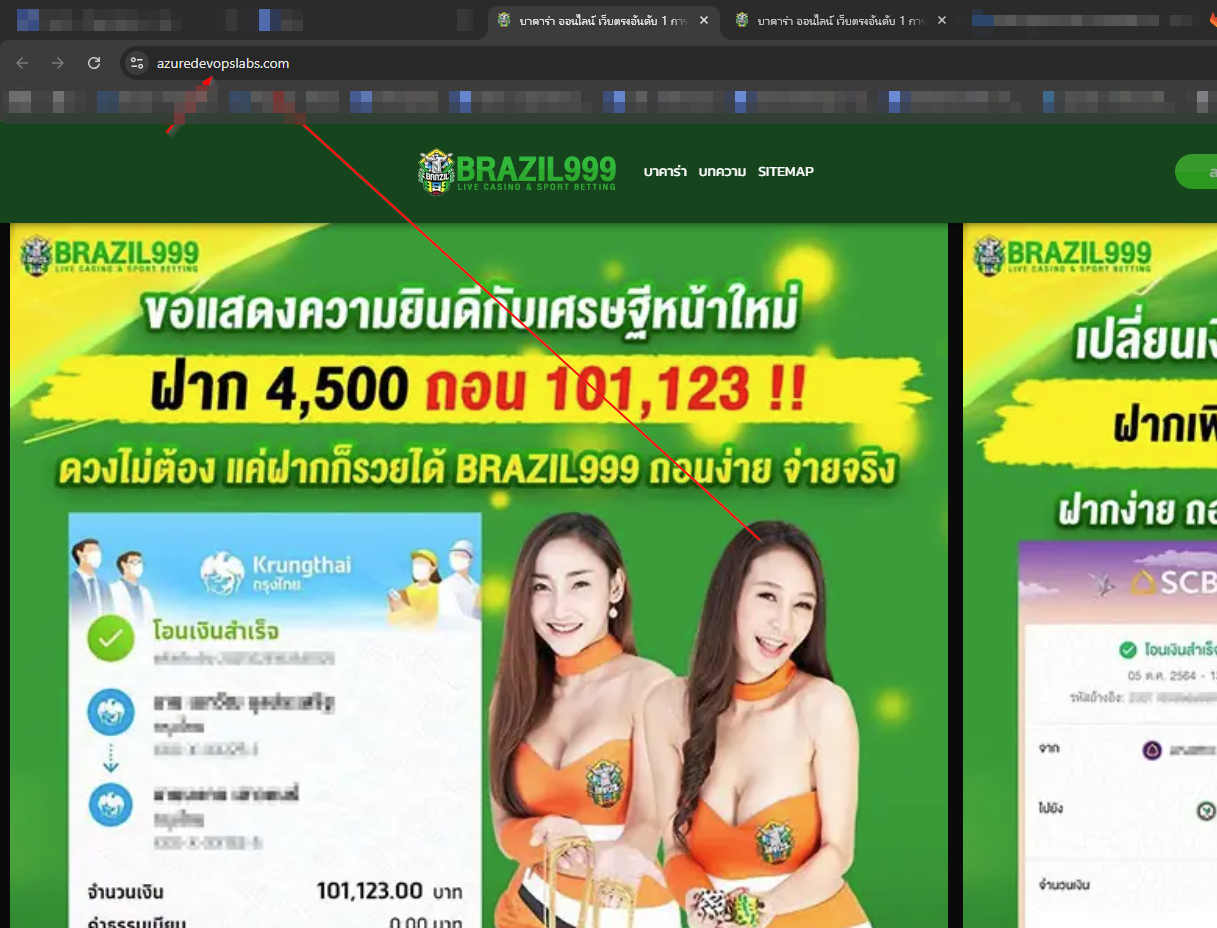
This is not a question, it’s a report. Jira’s JSM software currently contains links that point to phishing sites. I’m using this channel to report the issue because Jira does not appear to provide a public channel for reporting phishing within its software. The only option available is for organization administrators, which doesn’t make sense that only organization admins can report this. Most people who use Jira are operations staff, not admins, so they should also have a way to report phishing or security issues directly.