We have registered a whitelist for accessing only the URLs permitted by the internal Proxy.
OK https://company1.atlassian.net
OK https://api.atlasian.com (And other necessary domain)
NG https://myself.atlassian.net (User's personal website)
User cannot access myself.atlassian.net from company.
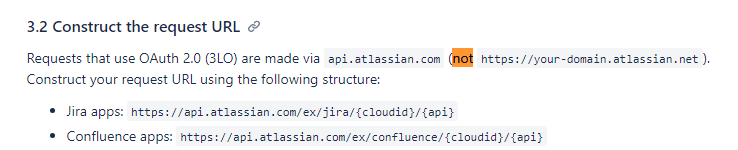
But if use a OAuth 2.0 app, can call api form api.atlassian.com/ex/jira bypass access to myself.atlassian.net.
Question:
Can I block rest api from OAuth 2.0 app in my proxy? I think two ways.
AND will anyelse affect to jira/wiki's normally use?
- block "api.atlassian.com/ex/"
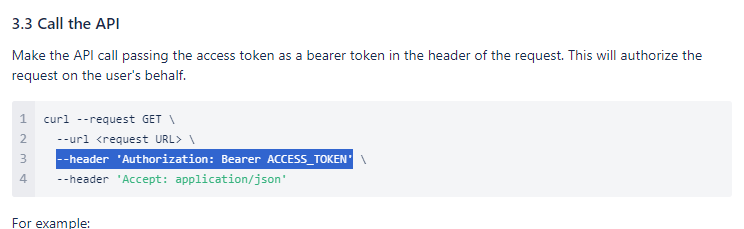
- block "api.atlassian.com" witch contain "Authorization: Bearer" in HTTP header
OAuth 2.0 document (3.2 Construct the request URL)
https://developer.atlassian.com/cloud/jira/platform/oauth-2-3lo-apps/