My company uses cloud Confluence and Jira and one of the employees wanted to make a page available for an external contractor.
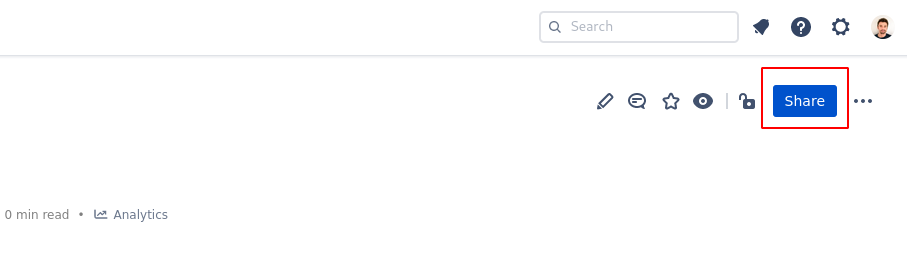
They legitimately, clicked the "Share" button on the top right and entered the external e-mail.
What happened next (as a reconstruction showed) was the external e-mail got an invite to join, and by joining, Confluence happily granted access to the entire space the page was in.
Weeks later, lo and behold, I notice we've got a new member with full rights as part of the team, although they are external. I am baffled at the choice of design of this feature, and the default settings for per-space permissions, and/or whatever else allowed this to happen.
Now that the harm has been done, I am asking for a way to check what that person has seen, here.
Also note that I see many post like this one which realise how the feature works but I haven't seen any post highlighting what a gross security failure this feature is.


