Hello,
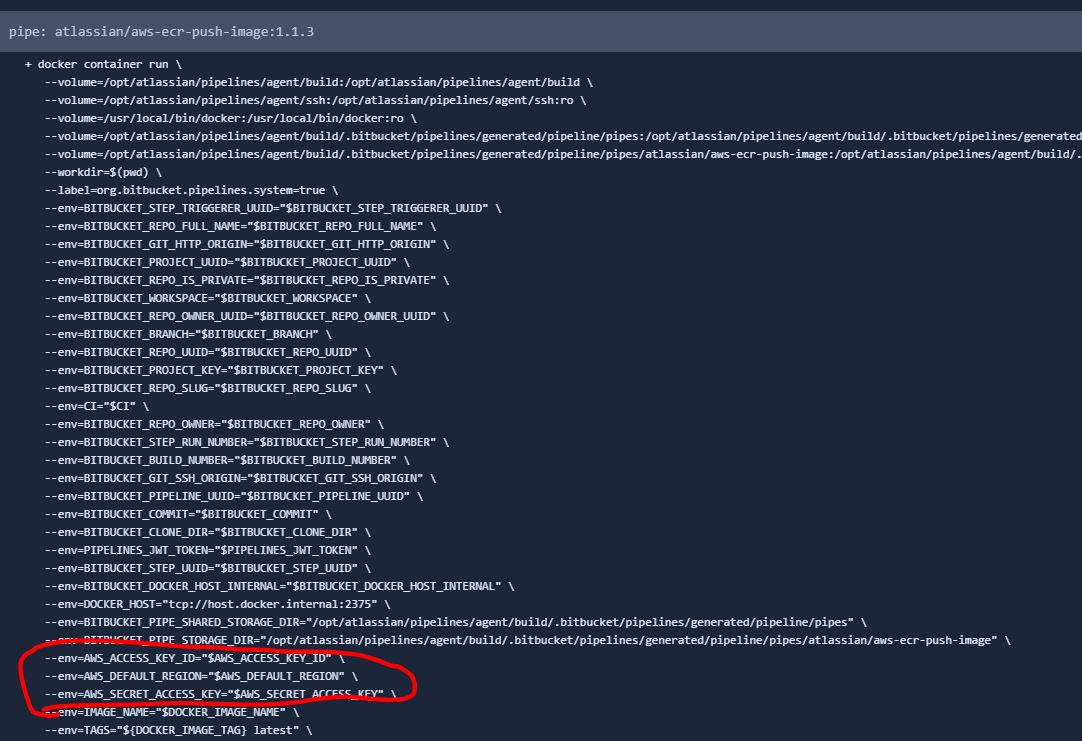
I am currently using the aws-ecr-push-image pipe to push my docker images to the elastic container registry. i see that when the pipe runs, all the environment variables that I stored on my bitbucket account are being attached to the image as build arguments.
I think this is a security issue since we have some variables which are supposed to be secrets and only used by bitbucket pipelines but these are instead getting attached to the docker image when getting pushed to the ECR.
So that means, anyone who uses that image can basically see those secrets when they use the container.