I'm trying to setup Nginx Reverse-Proxy for Jira Cloud application in order to make caching on our side because sometimes Jira Cloud works slowly for us.
I have configuration file below.
server {
server_name jira.company.local;
listen 80;
location / {
return 301 https://$server_name$request_uri;
}
}
server {
listen 443 default ssl;
server_name jira.company.local;
root /usr/share/nginx/html;
ssl_certificate /etc/nginx/cert.crt;
ssl_certificate_key /etc/nginx/cert.key; # self-signed
ssl on;
ssl_session_cache builtin:1000 shared:SSL:10m;
ssl_protocols TLSv1 TLSv1.1 TLSv1.2;
ssl_ciphers HIGH:!aNULL:!eNULL:!EXPORT:!CAMELLIA:!DES:!MD5:!PSK:!RC4;
ssl_prefer_server_ciphers on;
include /etc/nginx/default.d/*.conf;
client_max_body_size 10M;
location / {
proxy_pass https://company.atlassian.net:443;
proxy_set_header Host $host;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
}
error_page 404 /404.html;
location = /40x.html {
}
error_page 500 502 503 504 /50x.html;
location = /50x.html {
}
}
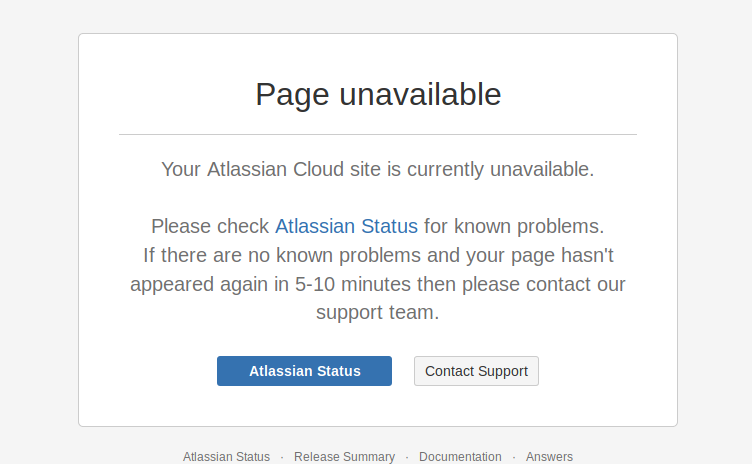
And it doesn't work.
I see error as on the attached screenshot.
Probably should I add/change something in Nginx configuration file?