Environment
- Identity Provider: Keycloak (SAML 2.0)
- Atlassian product: Jira Service Management (JSM)
- Domain verification: Enabled (verified domain)
- Provisioning method: JIT (Just-in-Time) via SAML
What I'm trying to achieve
I want first-time users to be automatically provisioned via JIT and land directly on a specific JSM Help Center/portal page after authentication. The goal is a seamless SSO experience where:
- User clicks a link (e.g., a ticket portal URL)
- Gets redirected to Keycloak for authentication
- JIT provisioning creates/grants their account access to JSM automatically
- User lands on the intended servicedesk page
The Problem
I'm passing the servicedesk portal URL (e.g., <base_url>/servicedesk/customer/portal/X) in the SAML RelayState parameter.
Observed behavior for first-time users:
- When
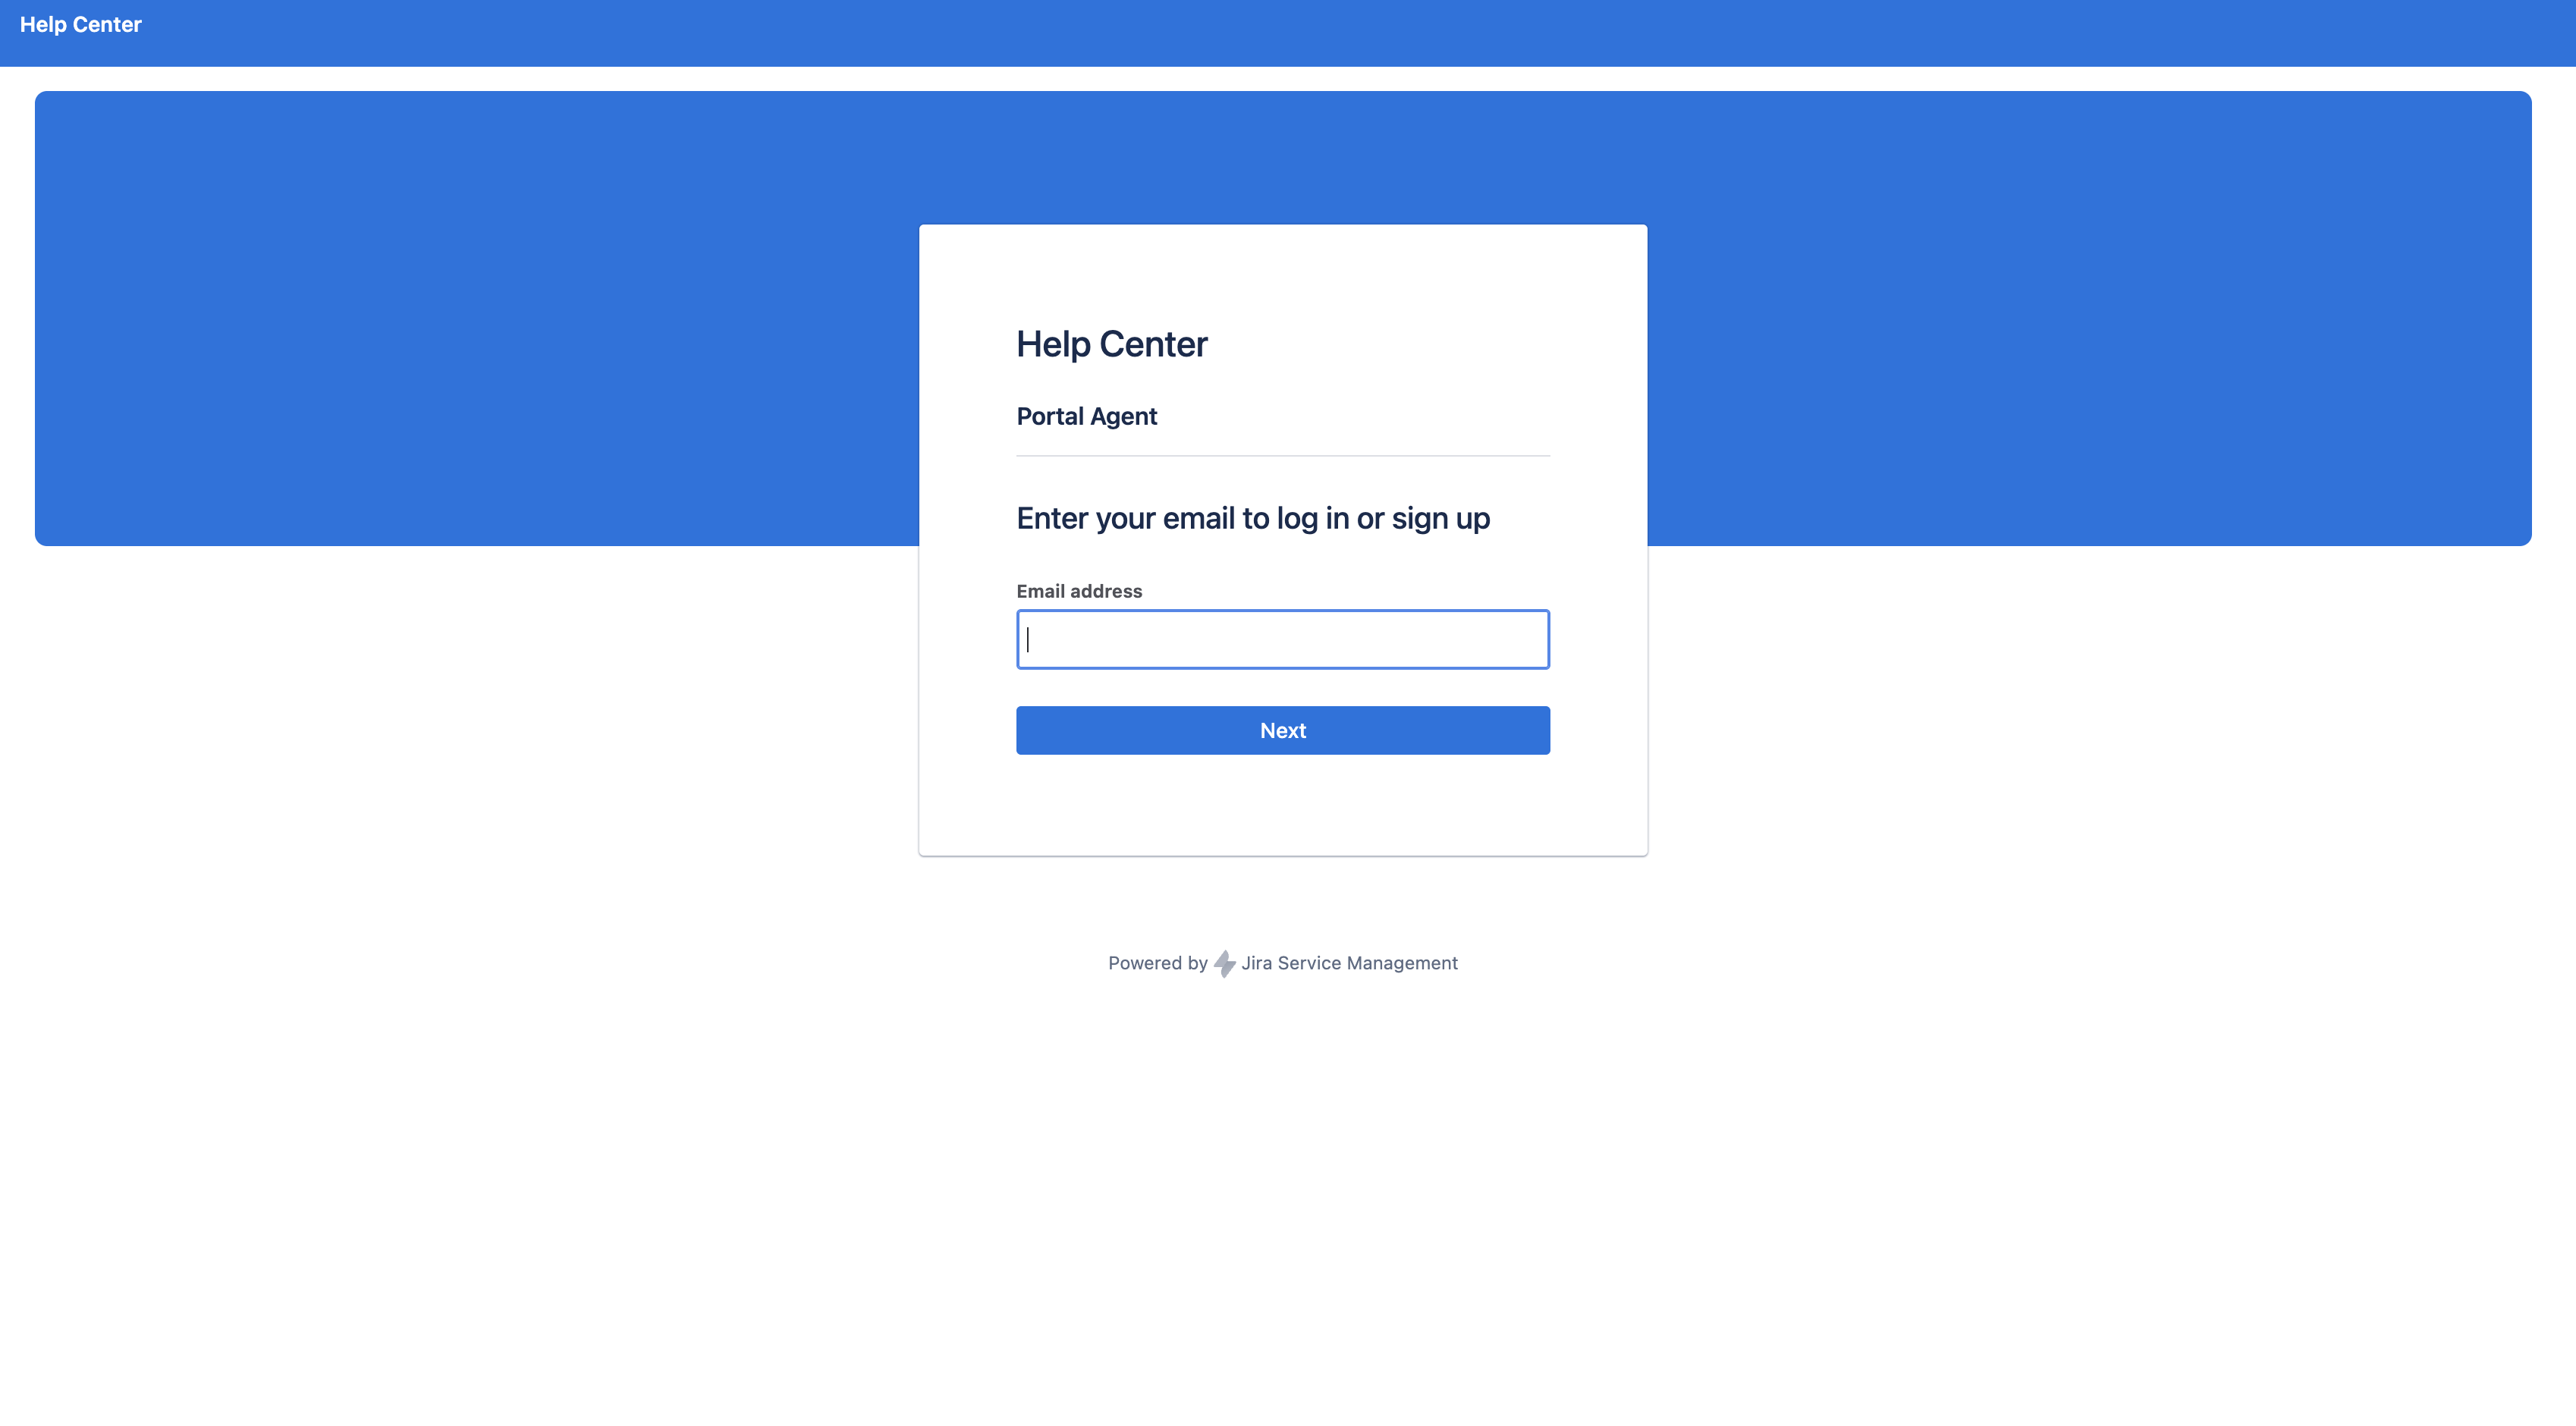
RelayState = servicedesk/portal URL → User is redirected to the Help Center login page instead of being logged in and taken to the portal
- When
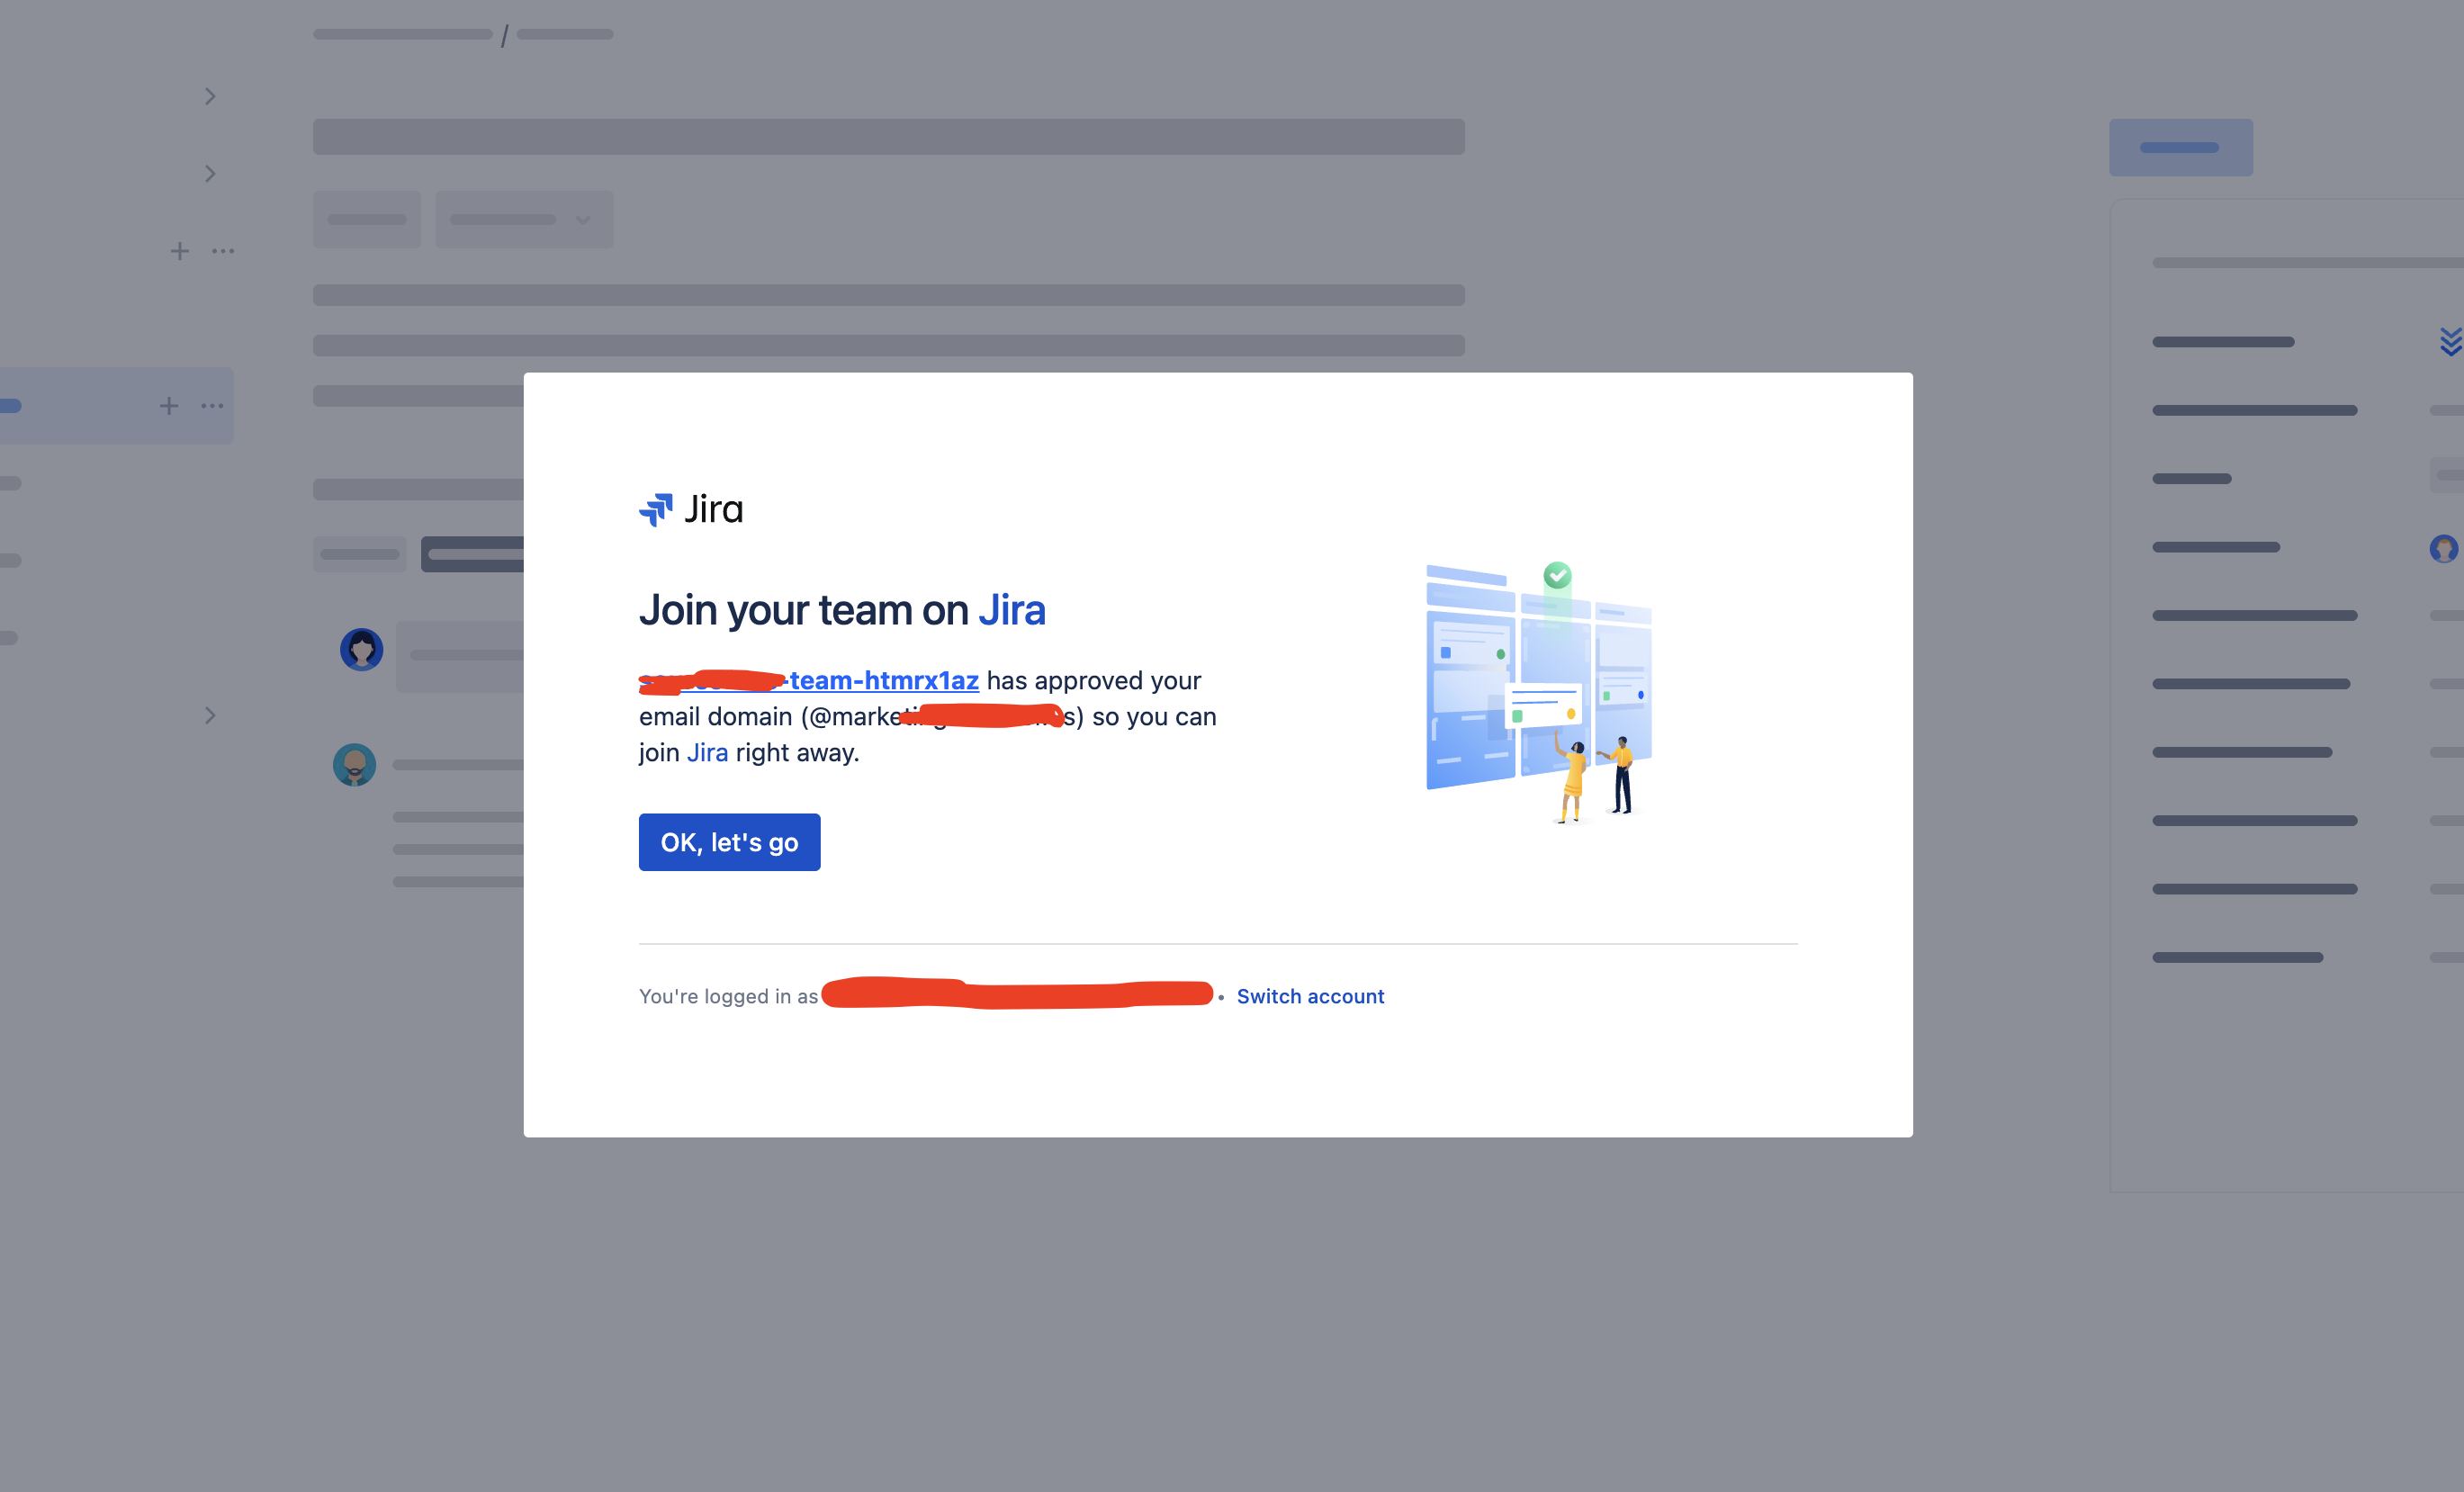
RelayState = <base_url>/jira (or any non-servicedesk URL) → User is shown a screen saying they "need to request access" — which is also not the desired behavior, but at least they're authenticated and can request access from there.
In both cases, returning/already-provisioned users land on the correct page without any issues. The problem is isolated to first-time JIT-provisioned users.
What I've tried
- Passing different variations of the servicedesk URL in
RelayState - Ensuring the SAML assertion includes the correct attributes for JSM product access
- Confirming that JIT provisioning itself works (users do get created in Atlassian)
Questions
- Is there a known issue or limitation with
RelayState and the JSM Help Center for JIT-provisioned users on their first login? - Is there a specific URL format or path that should be used in
RelayState to correctly redirect first-time users to the servicedesk portal post-provisioning? - Is there any recommended workaround — such as a landing page, a specific Atlassian URL that handles post-provisioning redirects, or a JSM-specific SSO entry point?
Any guidance from the community or Atlassian staff would be greatly appreciated!


