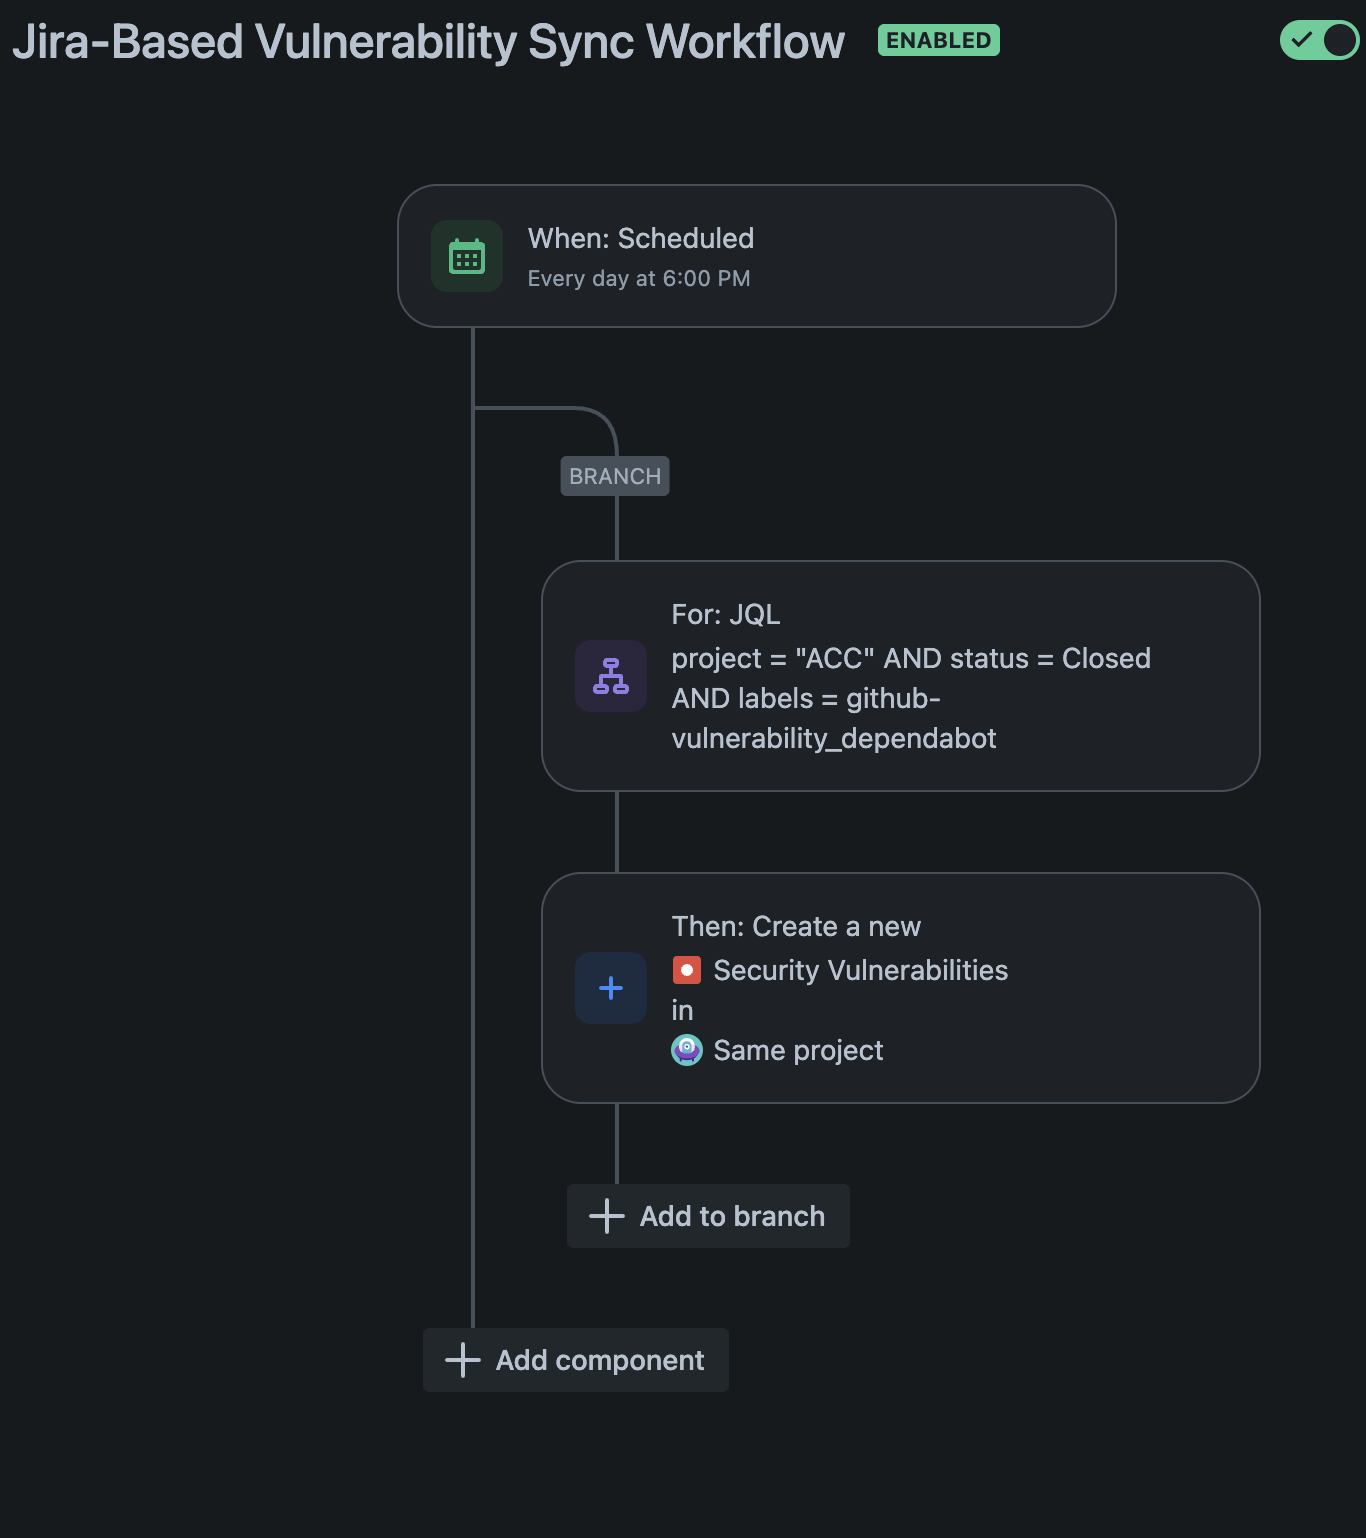
I'm setting up an automated rule in Jira to sync and track security vulnerabilities (CVEs) reported from GitHub via Dependabot. This is part of ensuring all CVEs remain visible and tracked until they're actually resolved.
The automation is mostly in place, but I'm facing issues with Steps 2 and 3 in the automation logic.
Current Setup:
Trigger: Scheduled every day at 6 PM.
JQL Condition: Filters for issues in the ACC project that are Closed and have the label github-vulnerability_dependabot.
Then: Create a new ticket under "Security Vulnerabilities".
And: Link the new ticket to the previous closed work item.
❗Problems Encountered:
3. Lookup step limitation:
I want to check if the same CVE is still being flagged in GitHub. The idea is to avoid reopening/resurfacing CVEs that are no longer valid.
However, Jira doesn't have access to updated CVE status from GitHub unless GitHub sends the updated status, and the "lookup issues" component isn't functioning properly—likely because the context (Work item) isn't produced earlier in the flow.
4. Validation before new issue creation:
We need a reliable way to compare the closed Jira ticket (with a given CVE ID) against GitHub’s latest open vulnerability list.
If the CVE still exists, only then should we create a new Jira ticket or reopen the previous one.
Could you help with how this cross-check (CVE still open?) can be added reliably to the automation logic before step 4 (issue creation)?