I'm trying to access Confluence Audit Records using the following endpoint wiki/rest/api/audit per these docs but am receiving 401 errors.
I've been able to successfully access Audit Records using Basic Auth for Jira and am using the same token I created in the Developer Console. In the 3LO app, I've ensured I have the read audit record granular scope checked.
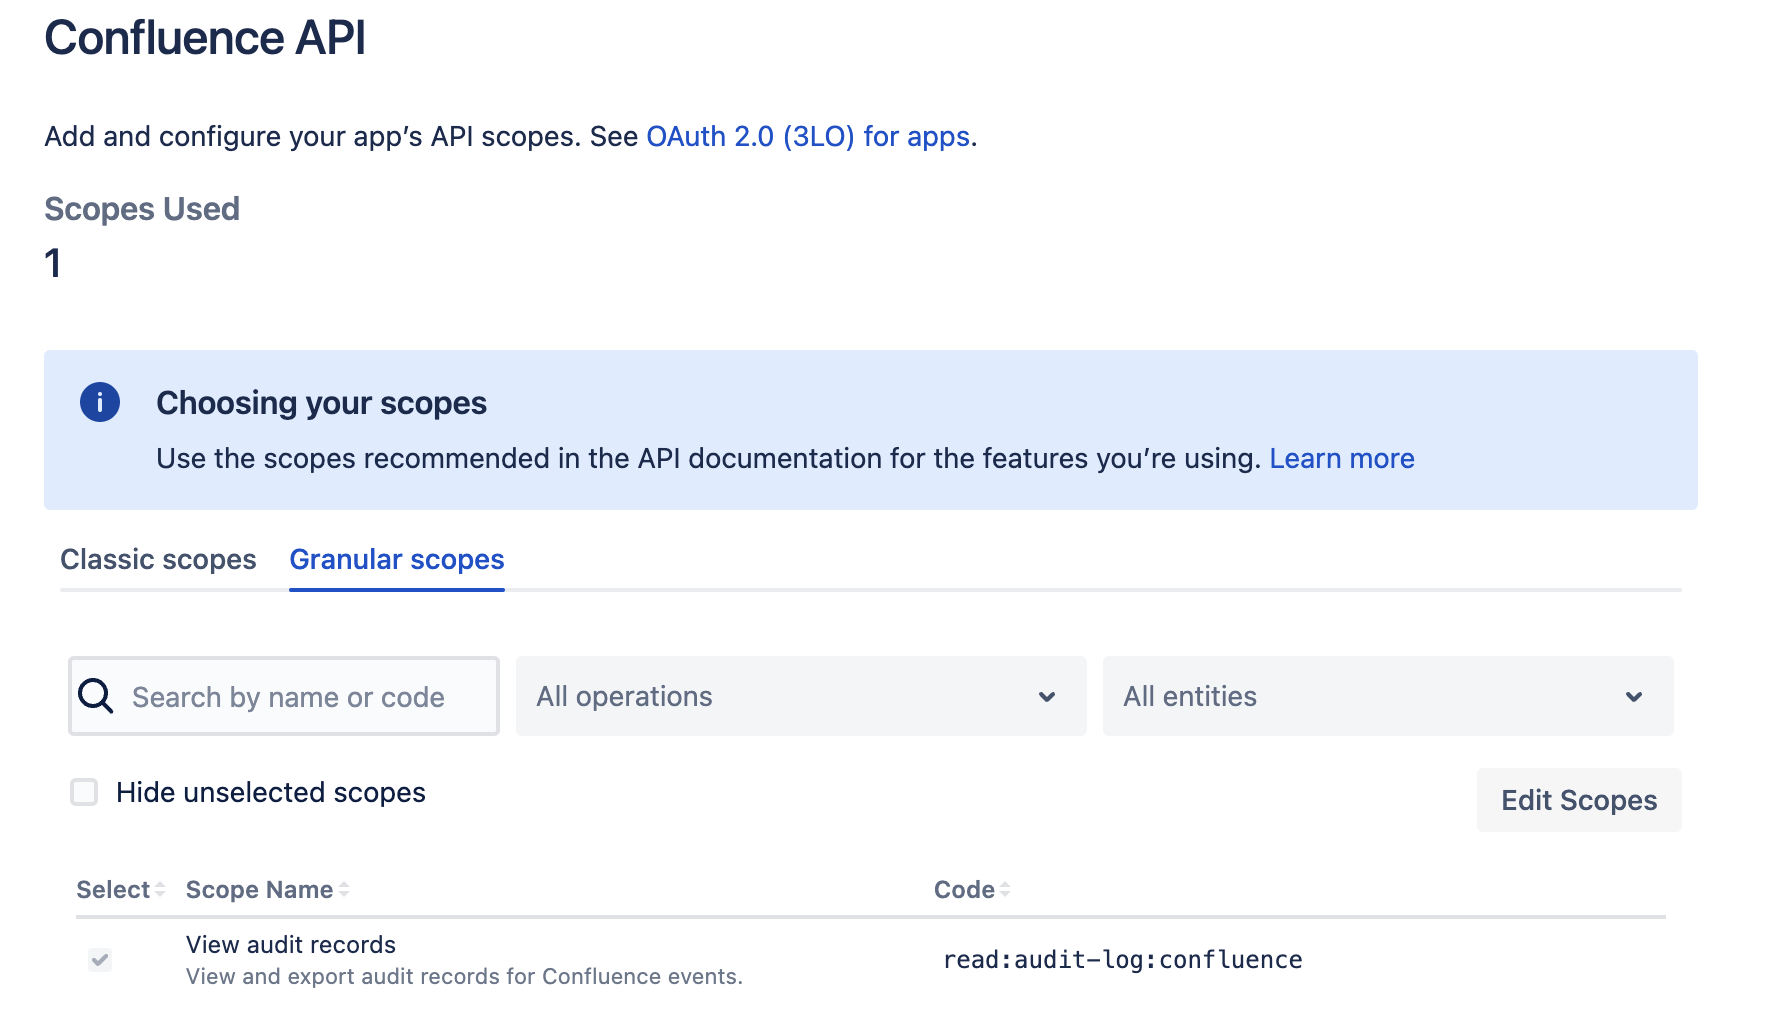
The documentation states that the Confluence Administrator' global permission is required, but my org is unable to grant me that permission. Instead, they've authorized my app, and believe this is sufficient.
The simple example I'm following for the CURL request from docs here:
curl -D- \

-X GET \

-H "Authorization: ${username:token}" \

-H "Content-Type: application/json" \

"https://${MY_SERVER}.atlassain.net/wiki/rest/api/audit"
Returns the following:
HTTP/2 302

cache-control: max-age=0, private, must-revalidate

content-length: 11

date: Tue, 22 Aug 2023 19:08:44 GMT

location: http://ww1.atlassain.net

server: Cowboy

set-cookie: sid={COOKIE}; path=/; domain=.atlassain.net; expires=Sun, 09 Sep 2091 22:22:51 GMT; max-age=${AGE}; secure; HttpOnly

Redirecting% ~ .......................................................................................... took 4s at 03:08:44 PM
When I run the CURL command from my Postman Instance:
curl --location 'https://${MY_SERVER}.atlassian.net/wiki/rest/api/audit' \

--header 'Accept: application/json' \

--header 'Authorization: Basic ${ENCODED_TOKEN}' \

<html>I get the following response:
<head>

 <title>Unauthorized (401)</title>

...
...
I've reviewed many similar questions in community help and am still not having any luck. I've ensured the password for my basic auth is the token from the Dev Console. Any help is greatly appreciated!

