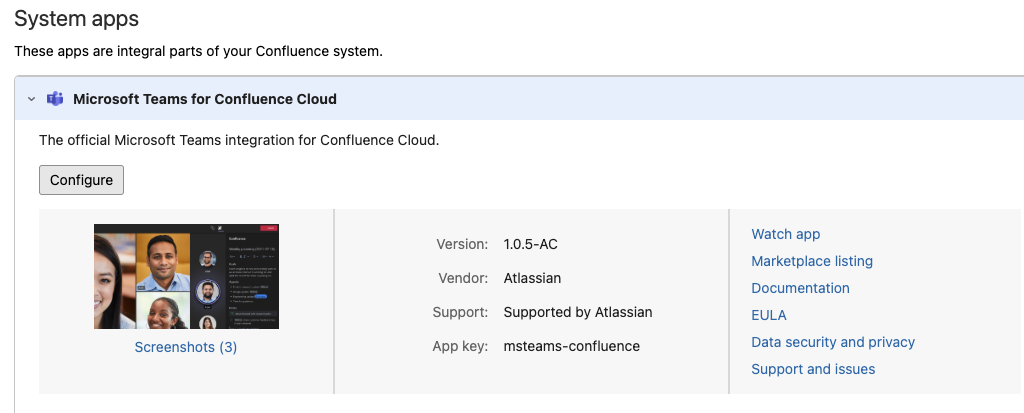
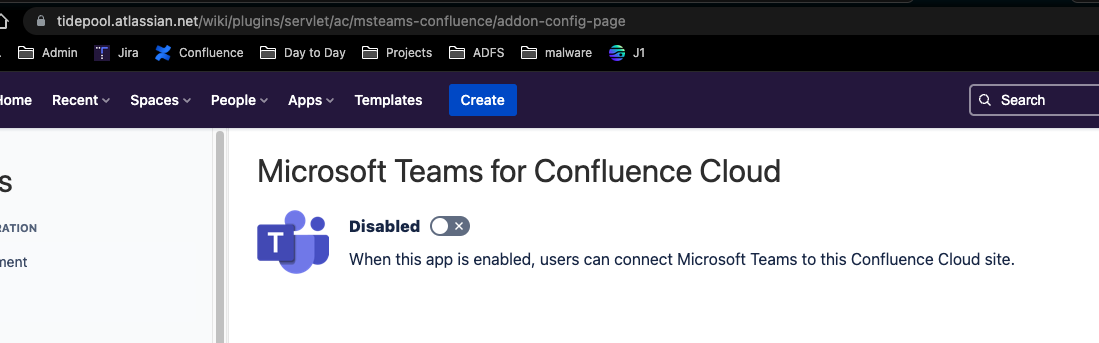
I wanted to see if anyone else was a bit surprised to see a brand new user showing up in their Space permissions with access enabled by default.
As a security engineer as well as admin for our Atlassian stack, I don't appreciate new users with granted permissions showing up unannounced and I wish there would have been a better way of handing that transparently.
It did end up costing me a couple hours investigating, ultimately disabling the plugin in the System Plugins and finding that this did NOT appear to remove the user and access permissions in all our Spaces, including private ones.
I really think this should have been an opt-in app, not enabled by default.
We would really encourage Atlassian to think about how they release new plugins with potential security implications and how these might be a cause for concern in environments that are extremely concerned about privacy.
My organization has a policy of reviewing all integrations of software, and this was never something we had the opportunity to review and had to spend time figuring it out after the fact.