Dear All,
so I'm strugling a little bit with Splunk and the Splunk Add-on for JIRA Atlassian Service Desk application.
I've succefully installed the plugin on my local environment and configured with basic autentication, my username and a PAT I've created bounded to my account.
Just in case, via curl on the same local machine I can call succefully for example the rest api
https://mycompany.atlassian.net/rest/api/3/project
curl --request GET --url 'https://mycomoany.atlassian.net/rest/api/3/project' --user 'name.surname@mycompany.com:GdfgdcdMZo0c5AiVmmYhD7E8' --header 'Accept: application/json'
I can see a well populated json starting with
[{"expand":"description,lead,issueTypes,url,projectKeys,permissions,insight","self":
etc etc, so the PAT is working, I've no connettivity issue and I my credentials are granted to perform tasks on Jira.
Anyway, when I'm configuring the addon on splunk side, everything goes wrong and I cannot manage to retrive nothing.
and I cannot find any kind of useful log at the moment
I've have an empty answer:
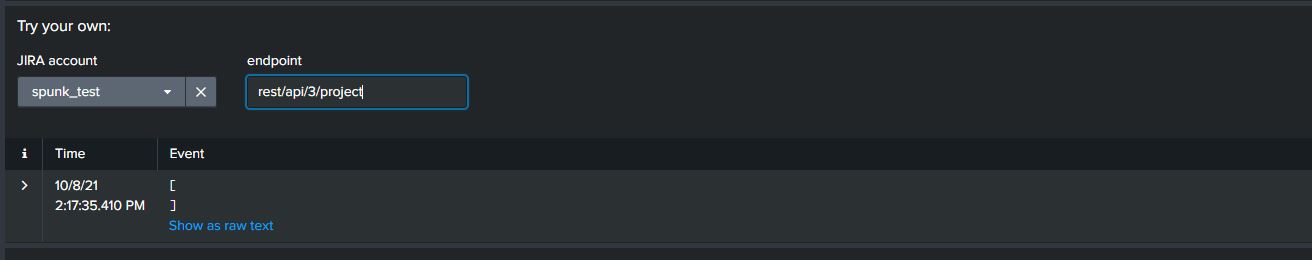
But from Splunk side I think everything is fine:
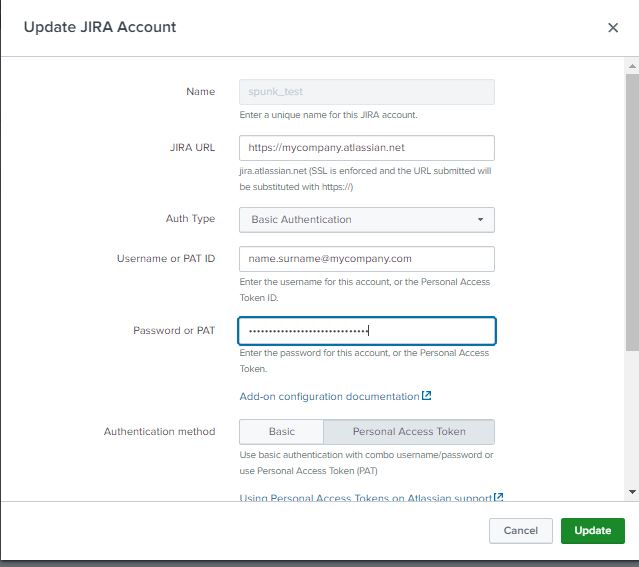
Obviously I've changed the actual values but, as I mentioned before, via curl it does work 
maybe I'm missing something very stupid but I don't know what else to think
Many thanks in advance, any help will be much appriciated
Marco

