In previous instances I had setup a Security Level of private to which I'd granted permission via project roles and group assignments. Typically issues would be private by default.
So if a user didn't have permission they couldn't see private issues. Clients wouldn't be in a group or Project Role which had permission.
Similarly if a client created an issue, the Security Level would be empty because they didn't have permission to set it. So they could see the issue.
I believe that behaviour has changed. Someone without permission to set the Issue Security Level creates an issue and the Issue Security is set to private and of course they can't see it.
Is my impression of the designed behaviour and use of it correct and regardless - how can I work around this?
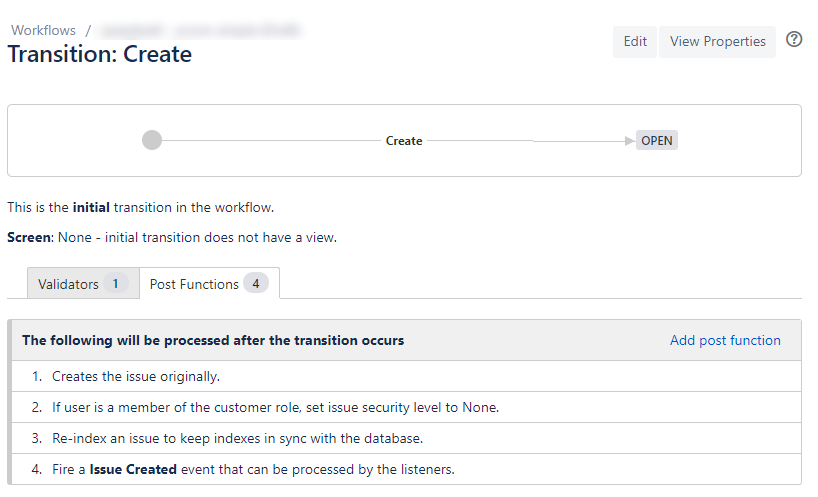
In an attempt to workaround this I've tried using workflow to set the level, but it doesn't work: