Hi everyone,
I am currently struggling with a permission/issue security issue I can't wrap my head around.
We want to restrict the issues in our project to only be viewed by the reporter. I was able to easily configure that with a new issue securty scheme which only grants permissions to our service desk team and the reporter.
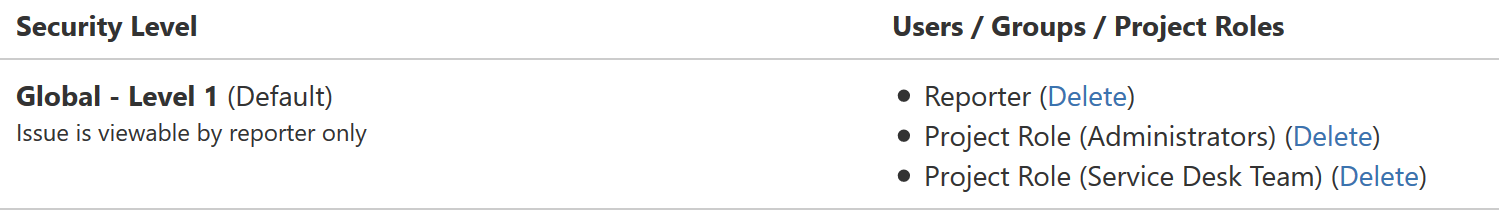
However what happens with that configuration is that another customer (same Organization) is not able to comment on an issue when he is not the reporter (comments via email). The following message is found in the processing log:
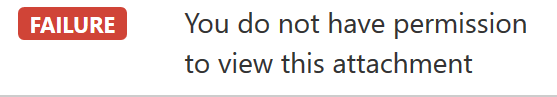
Additionally when I use the permission helper in the issue it complains that the user that can't comment is not member of my security scheme.
I know I can edit the issue security scheme to add another role or group to it and grant the customer the permission this way. However if I do that the customer can see all issues of his organization, which we want to prevent.


