Attempting a PoC of secrets scanning with the following setup. It reports success and that no secrets have been found (even though I would expect it to detect things are secrets) and interestingly the pipeline log has some pretty significant errors. Is it actually working as expected and just not detecting those lines as secrets or it if failing and falsely reporting success?
bitbucket-pipelines.yml
pipelines:
  default:
    - step:
        script:
          - pipe: atlassian/git-secrets-scan:3.1.0
secrets.txt
password=thisissupersecret
apikey=anothersecret
aws_key_example = AKIAIOSFODNN7EXAMPLE
github_token_example = ghp_abcdefghijklmnopqrstuvwxyzABCDEFGH1234
Results:
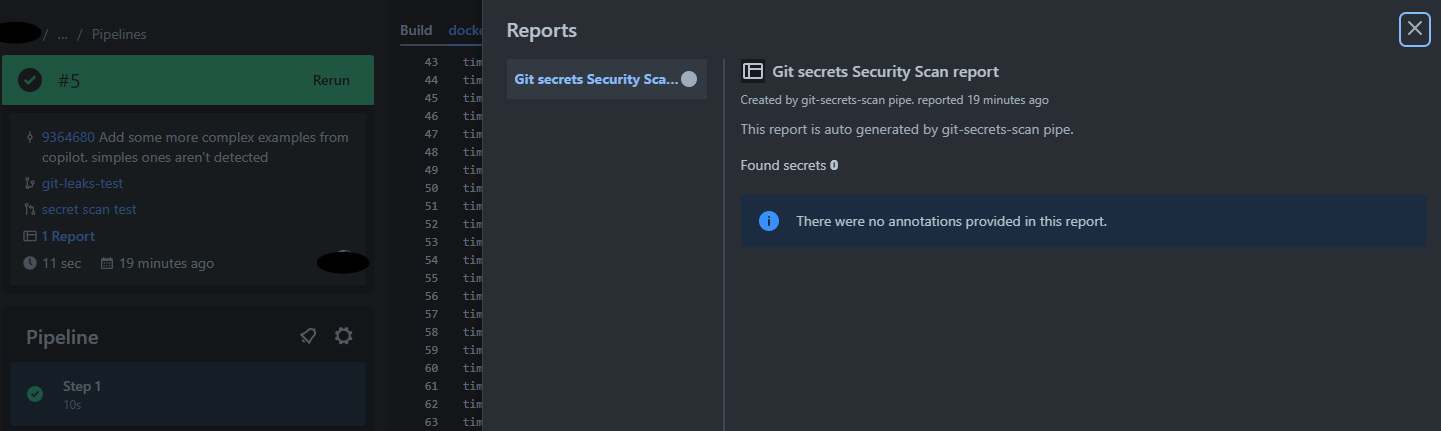
Log entries of concern:
<span>...</span>
time="2025-06-16T18:56:44.398829595Z" level=error msg="Handler for POST /v1.41/containers/create returned error: No such image: bitbucketpipelines/git-secrets-scan:3.2.0"<span>time="2025-06-16T18:56:44.373517654Z" level=error msg="AuthZRequest for HEAD /_ping returned error: authorization denied by plugin pipelines: "</span>
