I am still having issues with the 3.1.0 version of the git secret scanner pipe integration which I seemed to have faced in the previous versions too. The issue occurs when I try to include a .gitleaksignore file in my repository to exclude identified leaks.
Below is my configuration for the Secret Scanner, which uses default settings:
- step: &secrets-scan
   name: Run Secrets Scan
   script:
- pipe: atlassian/git-secrets-scan:3.1.0When this step runs on my repository, it correctly generates a report for a sample leak:
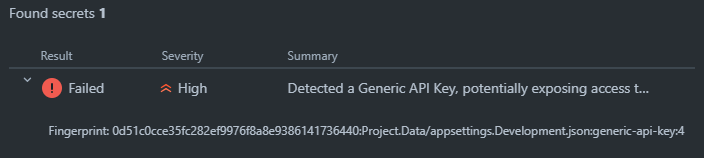
Next, I create a .gitleaksignore file in the root of my repository and include the exact fingerprint that was reported. When I commit these changes and the pipe reruns, I then get another failed scan and the same leak is picked up, but with a different fingerprint:
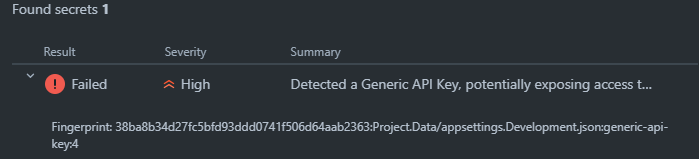
It seems that after each commit, the fingerprint of this leak changes, potentially causing issues with the .gitleaksingore file correctly ignoring it.
I have tried this with a separate repository and a separate list of leaks, and the same issue occurs. Can you advise if I am following the correct process? I believe this should be working as per my workflow. But I'm confused as to why the fingerprints in the report would be different with each pipe run.


