SO WHY ARE ATLASSIAN FOCUSING ON SECURITY IMPROVEMENTS?
It is no surprise that Atlassian has been focusing on their cloud platform ever since the announcement of Servers end (and before in my eyes). But while a lot of us can make use of their SaaS application, there is still a lot of their customers that due to regulations or current security requirements cannot touch it, no matter how much Atlassian wish they could.
WHY DO A LOT OF BUSINESSES SEE IT AS A BLOCKER?
Unfortunately in this day and age, security standards are a necessity to help keep both companies & individuals safe from exposure. The better the security of the application the more the company can trust and therefore use it.
With certain industries having higher requirements than others, businesses are not going to open themselves to legal action or possible attacks if the platform does not meet ALL components required.
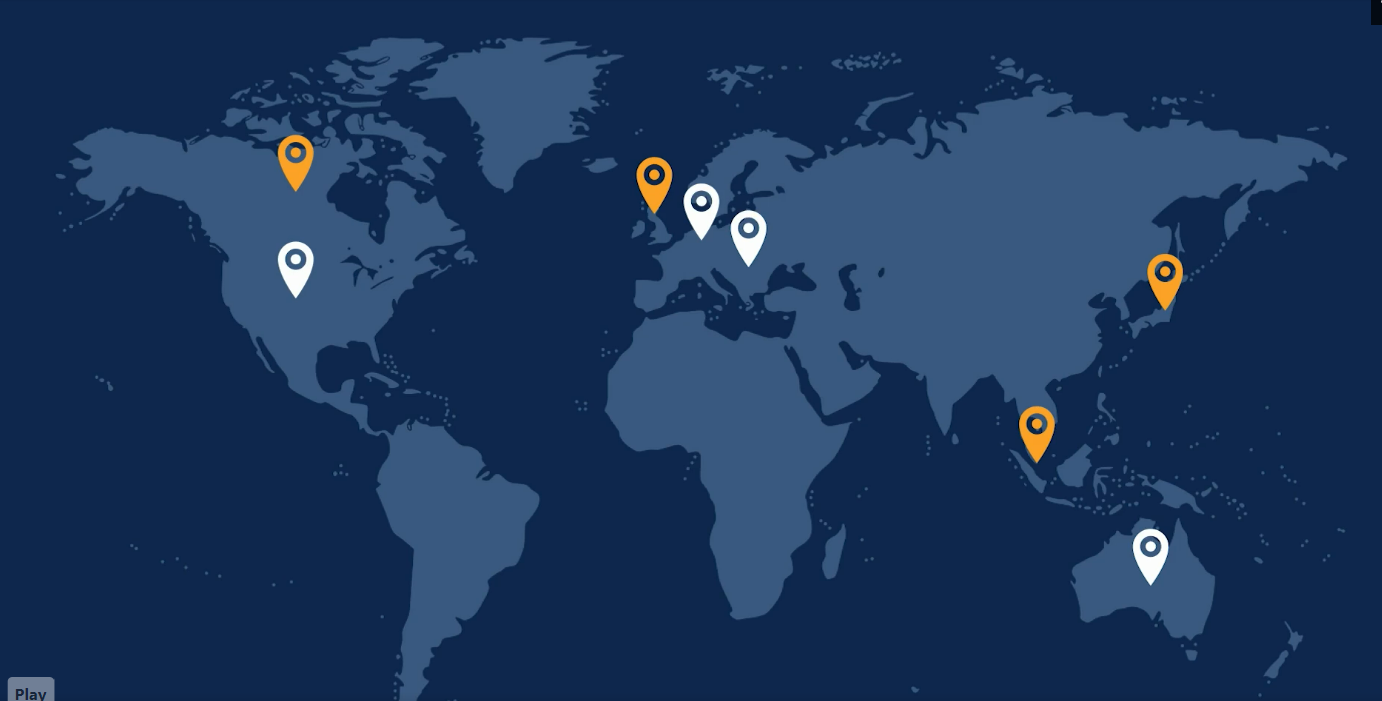
This can be as simple as data residency or regulatory body compliance like HIPPA or FEDRAMP. Without these requirements met, the company just simply will not use the cloud product.
Governments and regulatory bodies across the globe have recognized the escalating risks of cyber threats, promulgating stringent regulations to protect consumers and their data. Companies that prioritize new security features in their products demonstrate a commitment to compliance and adherence to legal obligations, mitigating the risk of penalties and legal ramifications.
WHO ARE THEY TARGETING WITH THESE UPDATES?
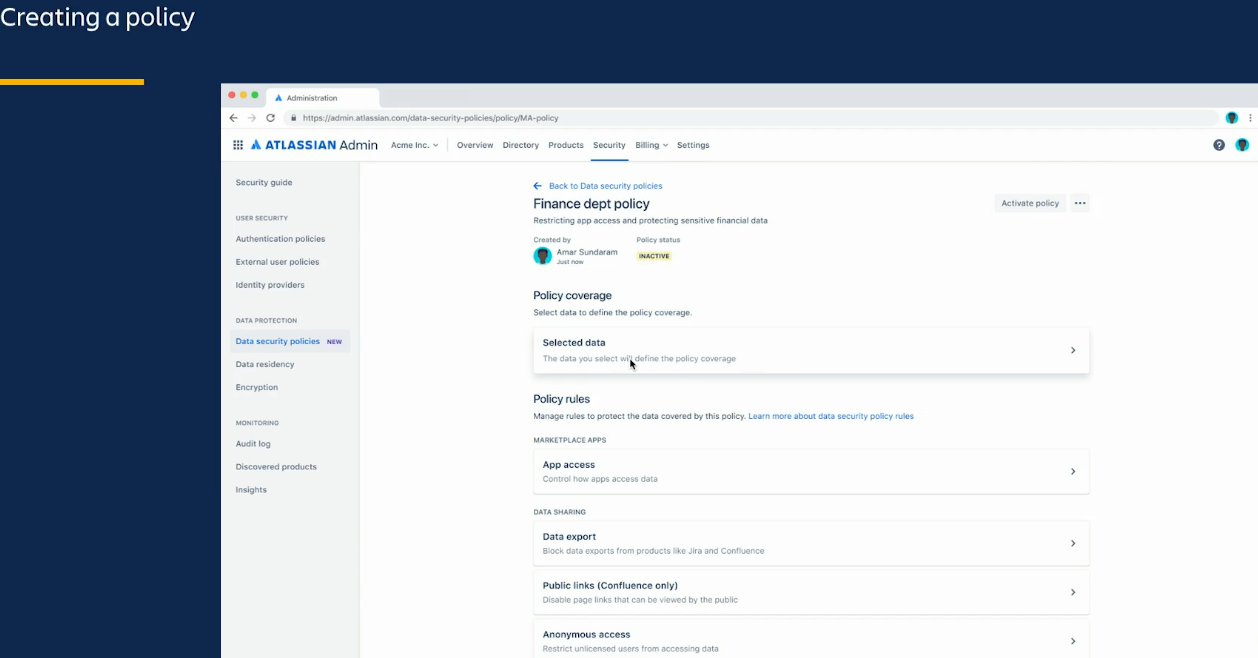
With this in mind, Atlassian are doing everything they can to remove the barriers for entry to cloud. Atlassian is investing in the security features around data residency, regulatory body compliance and proactive functionality that helps reduce attack vectors.
Companies are always looking for better proactive measures over anything else. The more the company can do upfront to mitigate the open number or attack vectors the better.
While a lot of their current cloud users, including me, are looking forward to see the updates hit their sites, the bit target for them is those that just simply cannot use the platform without them. With the EOL of server fast approaching, Atlassian want to get these features in so migrations can happen before February 2024.
WHERE DO I SEE THIS GOING?
Atlassian will continue to invest in security, not only for the necessity of the platform for customers to continue feeling the platform is security and reliable but in order to remove all barriers of entry for the cloud product.
It is incredibly clear Atlassian are a cloud first company. Almost all new functionality goes into the cloud product first. In order to continue increasing the customer base, Atlassian need to remove all barriers so all industries and companies can now use it.
WHAT ARE THE LARGE SECURITY IMPROVEMENTS COMING?
API ACCESS RESTRICTIONS
This new functionality will allow admins to block API request being made by certain Atlassian accounts. API tokens will be able to be made by managed accounts to and from certain products.
View this on the roadmap
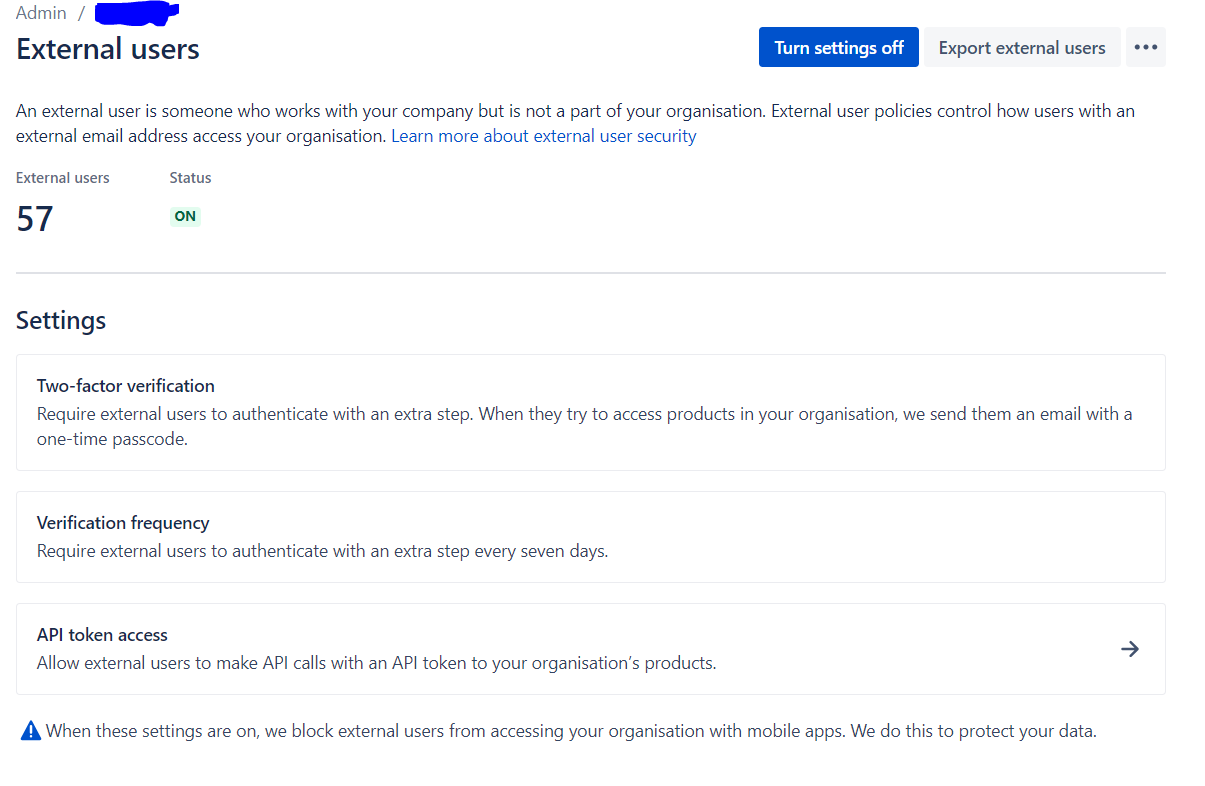
EXTERNAL USER SECURITY MANAGEMENT - JUST HIT GENERAL AVAILABILITY
Currently, the only way of ensuring a level of security for your users is to manage them. However, we often find ourselves working with third parties on a regular basis and onboarding every single user is time consuming and not really a viable option. Luckily Atlassian did recognise this (after a lot of feedback). External user security now allows unmanaged users to still have controls like 2fa or soon, SSO capabilities enforced helping to keep company data safe. This will only launch at first with the 2fa control with SSO joining in the latter parts of 2023.
View this on the roadmap