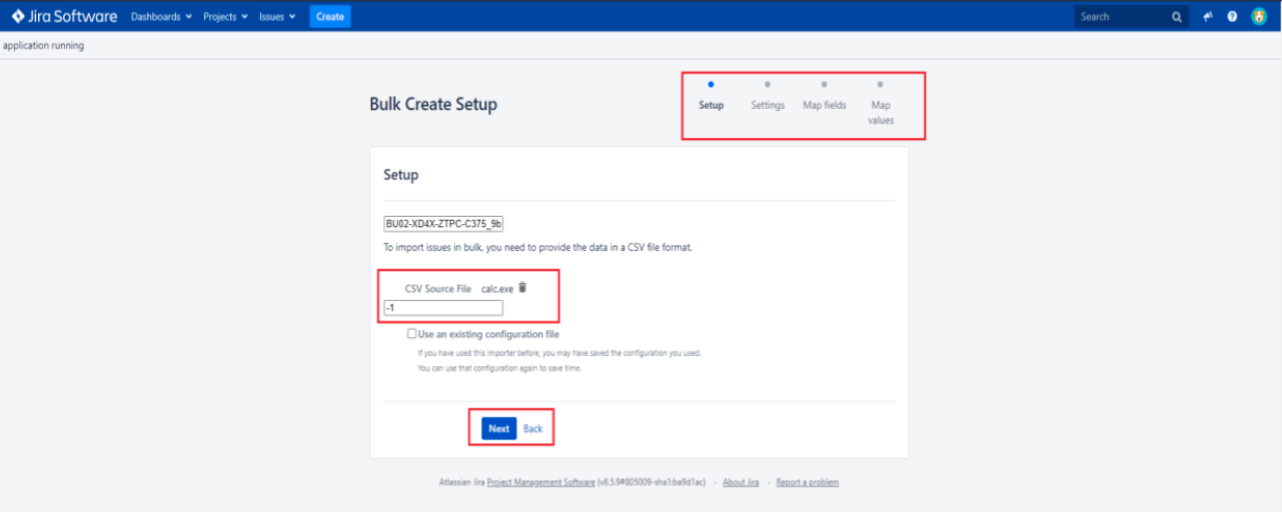
During Assessment it was observed that application allows malicious files to be uploaded.
1. Malicious files can be uploaded with multiple extensions as file content is not validated.
2. Eicar virus file can be uploaded.
Impact :
A remote attacker could send a malicious file via POST request with a specially crafted filename, file content or mime type and execute arbitrary code to take complete control of the victim’s machine/server. The consequences of unrestricted file upload can vary, including complete system takeover, an overloaded file system or database, forwarding attacks to back-end systems, client-side attacks, or simple defacement.