Hello there,
We are looking for information, best practices and/or recommandations regarding authentication using Rest Api while trying to add some impersonation.
We have an architecture with external applications creating Jira issues through a microservice developped internally that is accessible behind a WSO2 API Management gate.
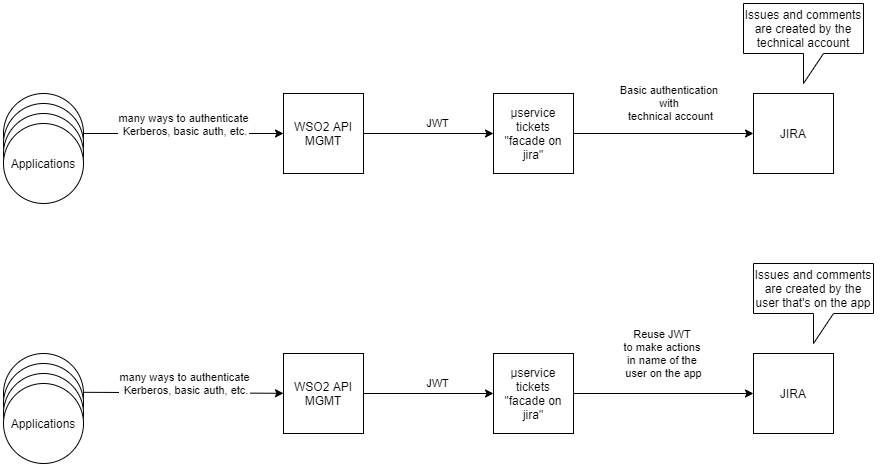
We are using JWT token to identify the user from the external Application to the microservice.
For the time being, our microservice is using Jira RestApi with a specific technical account, always the same.
We aim at making every Rest Api call to Jira with the "real user" from the application (impersonation).
Any feedback, rex or documentation you may have will be welcome !
Thanks.

