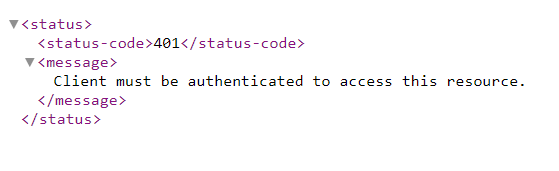
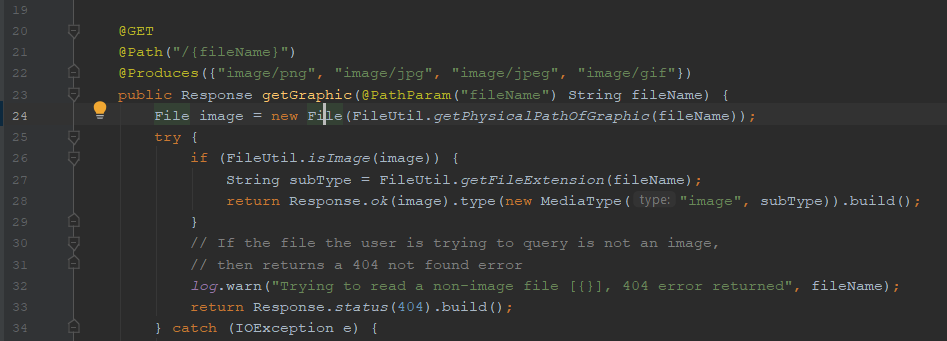
I have a REST API inside my jira plugin, without @AnonymousAllowed annotation:
My question is: How can I custom 401 response when an unauthorized user try to access my resources, such as redirect them to another page, or send them a HTML page,... instead of just send a xml error. Thanks a lot for your help.