Hello,
I haven't been able to find any informations about this particular questions. I have done synchronizations itself with AD numerous of times, but now I am struggling a bit with this scenario:
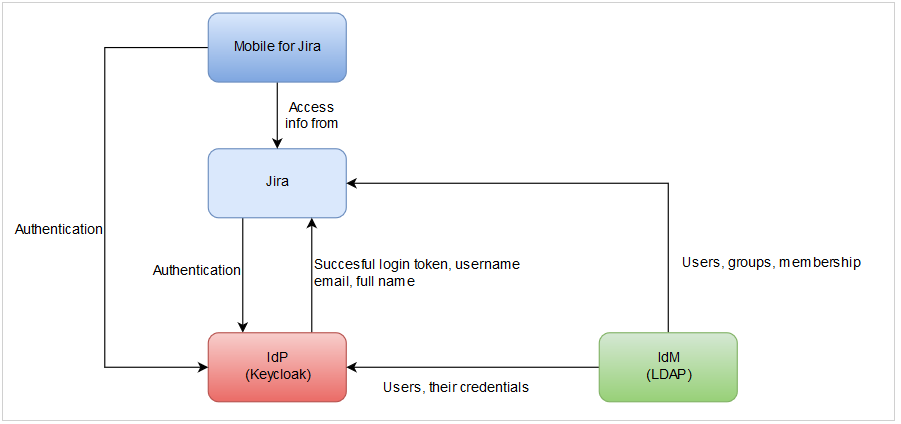
Authentization in our network is done against IdP called Keycloak. We use Kerberos and we can force 2FA over Keycloak to certain users (as thats why we use it). Keycloak itself is federating users from LDAP and all things connected to users (groups, membership) is done directly in LDAP. Keycloak is also federating some other users from other systems, thats again why we use it.
Now I am struggling with Jira itself. When I autheticate against Keycloak, all I get is information about that given user (e.g. about his roles, his credentials etc.). But these roles must exists already in Jira as groups. Same applies to users themselves (as I don't want the users to be created automatically, if they don't exist, partially because user is authenticated everytime, even shouldn't have access to Jira). How can I get all the groups inside Jira, when Keycloak is unable to work as LDAP itself (or maybe I am missing something?)
What we want to achieve:
- Federate all users from different systems (but most of them are in LDAP, like 99%) in one IdP system (which is currently Keycloak).
- Create groups (or roles or whatever is best name for it) in one system and also manage membership for these groups.
- Manage system access at one place (which should driven by some groups user belongs to - e.g. if user belongs to jira-core-users, he has access to Jira Core, if I add a new group "called" test, group should be created in Jira, and if I add user to this group, his membership should be synchronized to Jira too).
What we did now is that we added synchronization directly with LDAP (which help us achieve request number 2. and 3.) and authentication is done trough one of the SAML SSO plugins available on marketplace.
We struggle now, that user is able to login directly to Jira, because all his credentials are now in Jira. We are able to redirect automatically to Keycloak login, but then the are other places, where he can still login directly into Jira (e.g. app Mobile for Jira).
Rather that making a hack solution not to store passwords in Jira or not authenticating against LDAP, I want to achieve proper clean way to these three points. I am unsure that synchronizing LDAP to both Keycloak and Jira is needed, but I don't see any other solution how can I manage groups in LDAP.
Does anybody came across similiar problem, or maybe I am just misunderstanding the whole problem at all.
Actual status is drawn here: