I'm using SCIM to provision users and groups to my Identity Provider (with verified domain) in Atlassian. I'd like to grant app access to the synced groups, but I'm not seeing any way to do that. Is this possible?
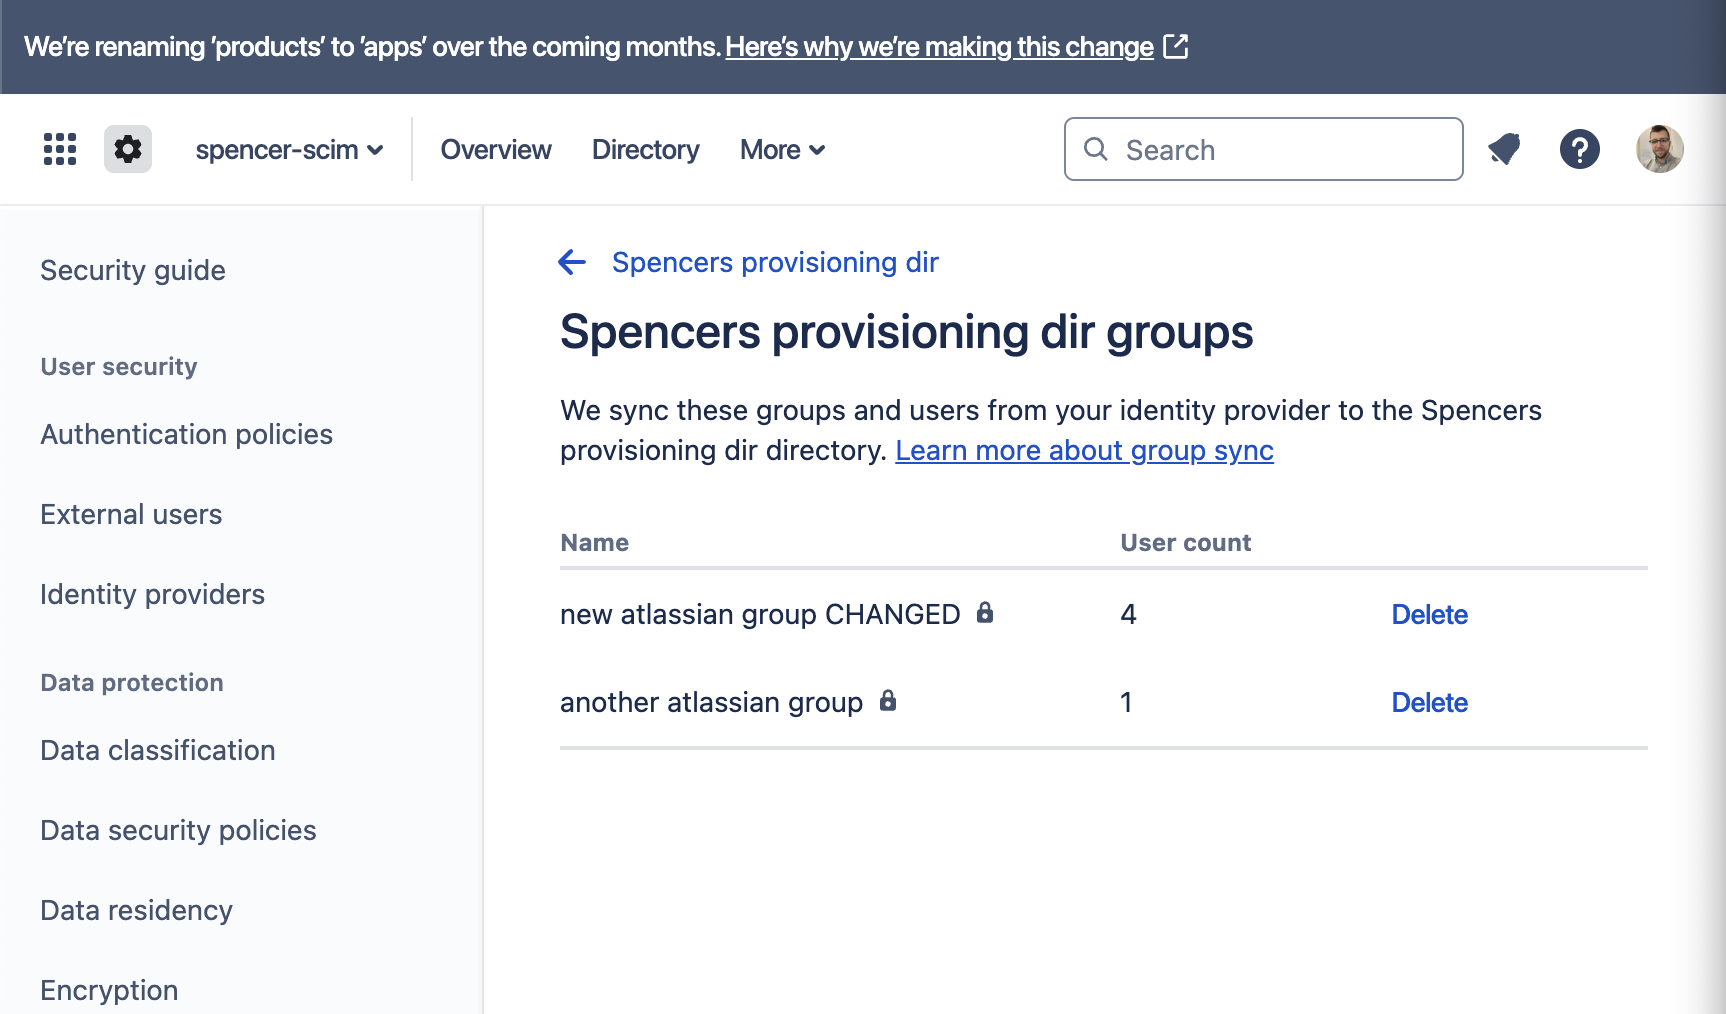
Navigating to Security -> Identity Providers -> <my_idp> -> View Groups, I can see the groups I synced over for testing, but see no way to assign app access to them. Delete is the only option.
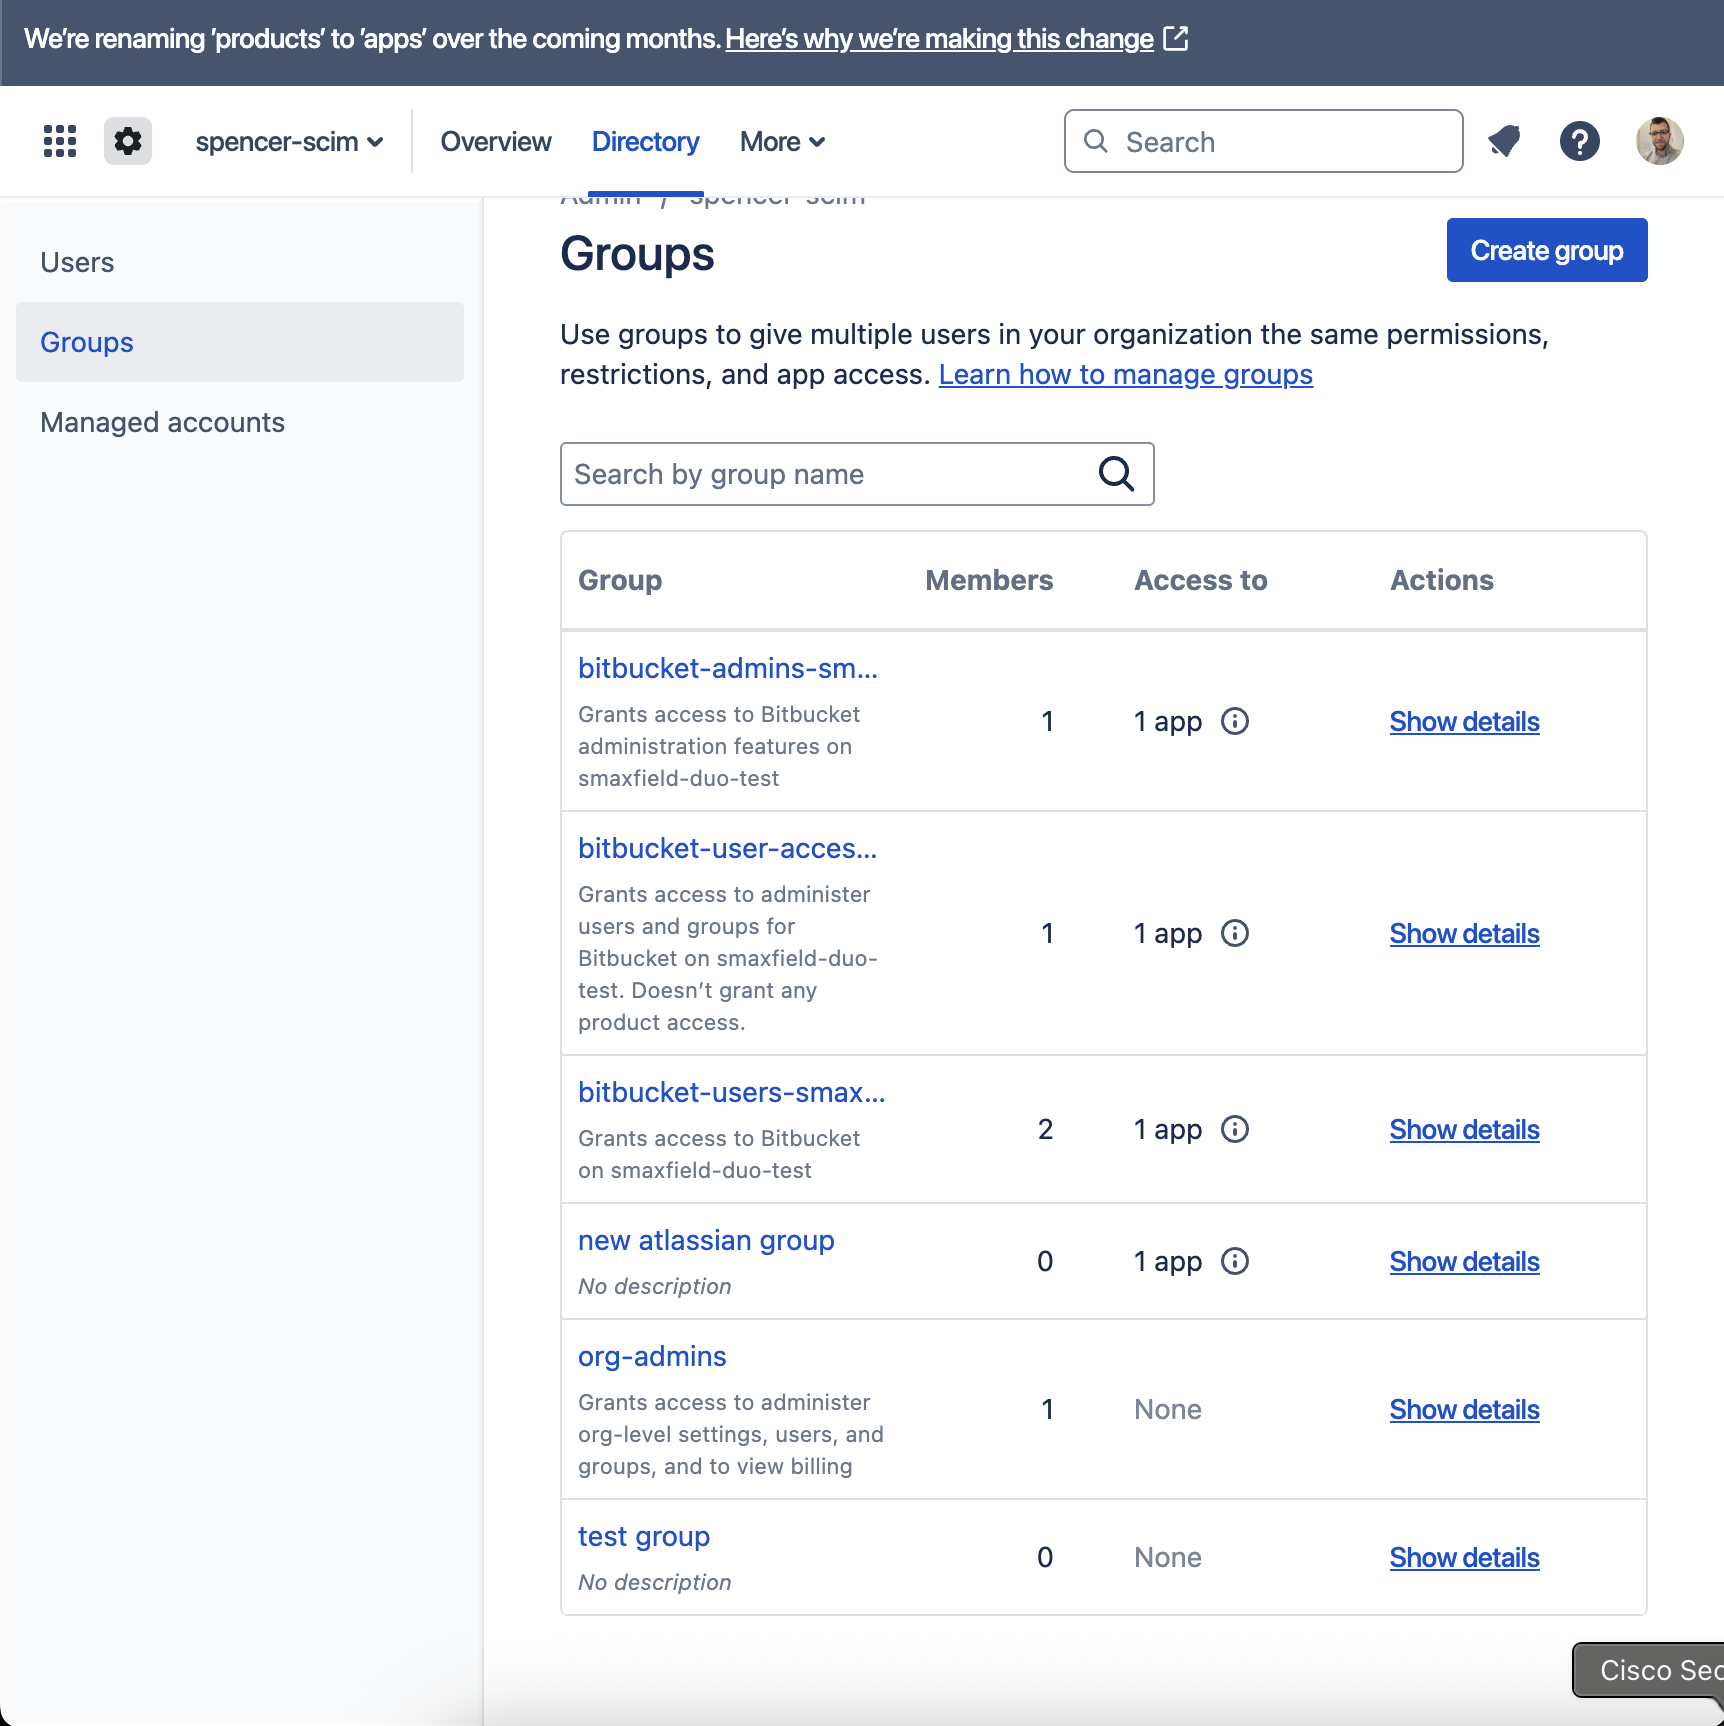
If I go to Directory -> Groups, the synced groups are not shown there, so from this view I'm only able to add app access to non-synced groups
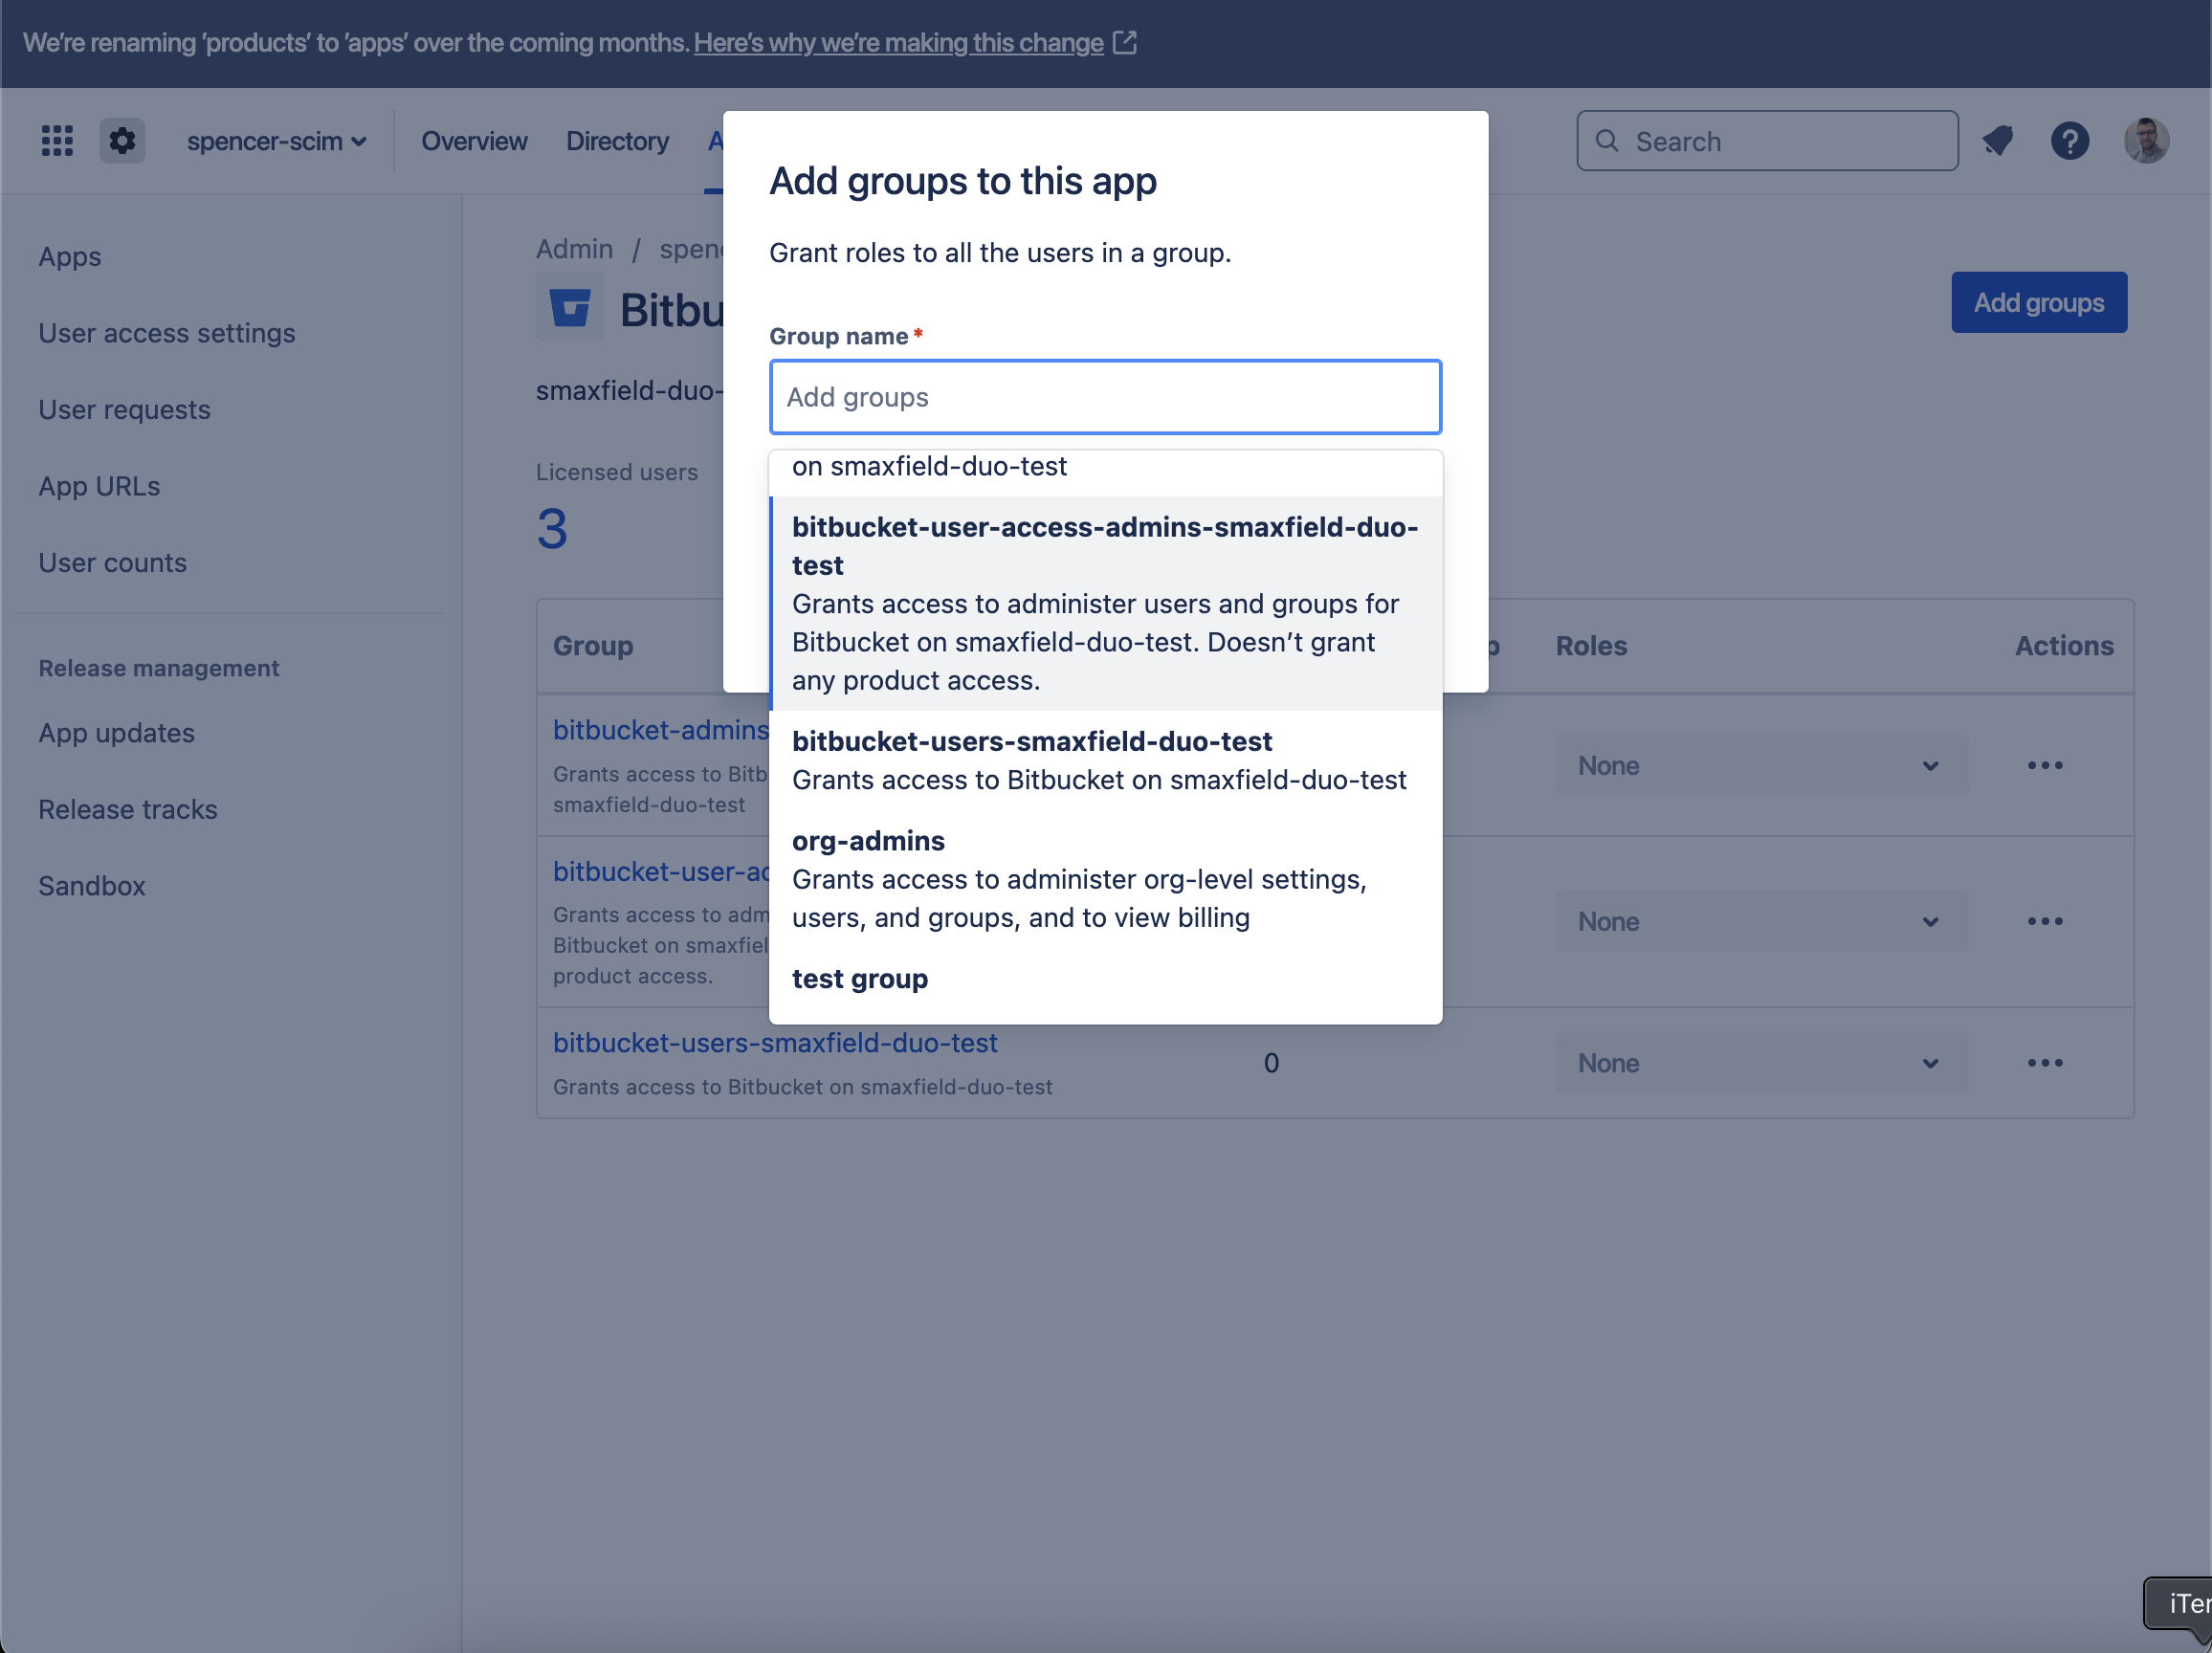
I also thought the Apps page might allow what I'm attempting, but that doesn't work either. Only non-synced groups show in the dropdown when adding a group to an app. Using my Bitbucket app as an example and clicking `Add Groups`:
How can I add group access to my IdP synced groups (e.g. 'another atlassian group') in the same way I'm able to add them to non-synced groups?


