I have access keys and secrets defined as bitbucket workspace secret variables. One variable pair for dev and one for prod environment:
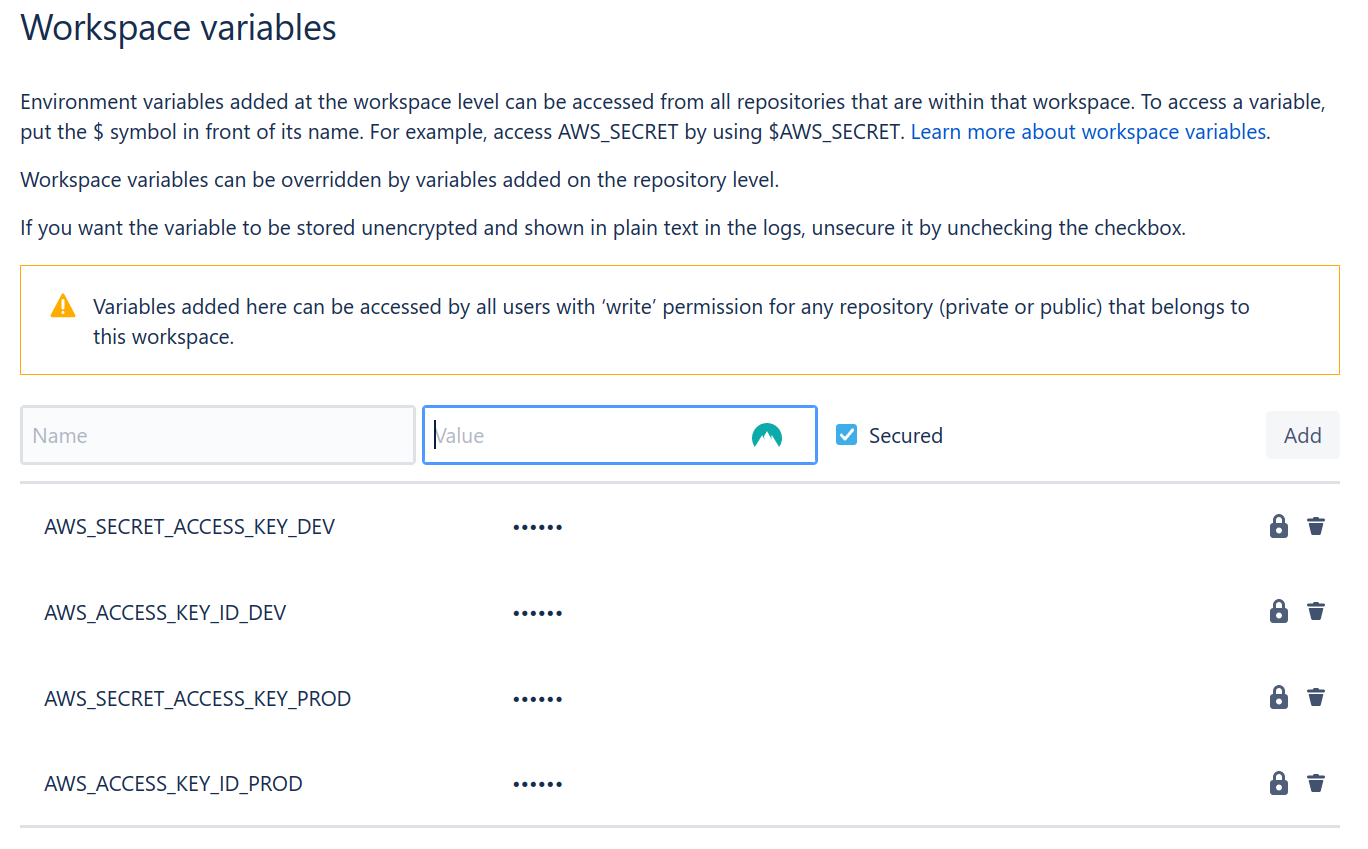
Our system admin manages and rotates these keys, and multiple repositories utilizes these in the pipeline.
In one of the repos I'd like to reuse the DEV postifxed variables without the postfix, as repository variables.
I tried to do this in Settings/Pipelines/Repository variables page with defining the next variables:
- AWS_ACCESS_KEY_ID: $AWS_ACCESS_KEY_ID_DEV
- AWS_SECRET_ACCESS_KEY: $AWS_SECRET_ACCESS_KEY_DEV
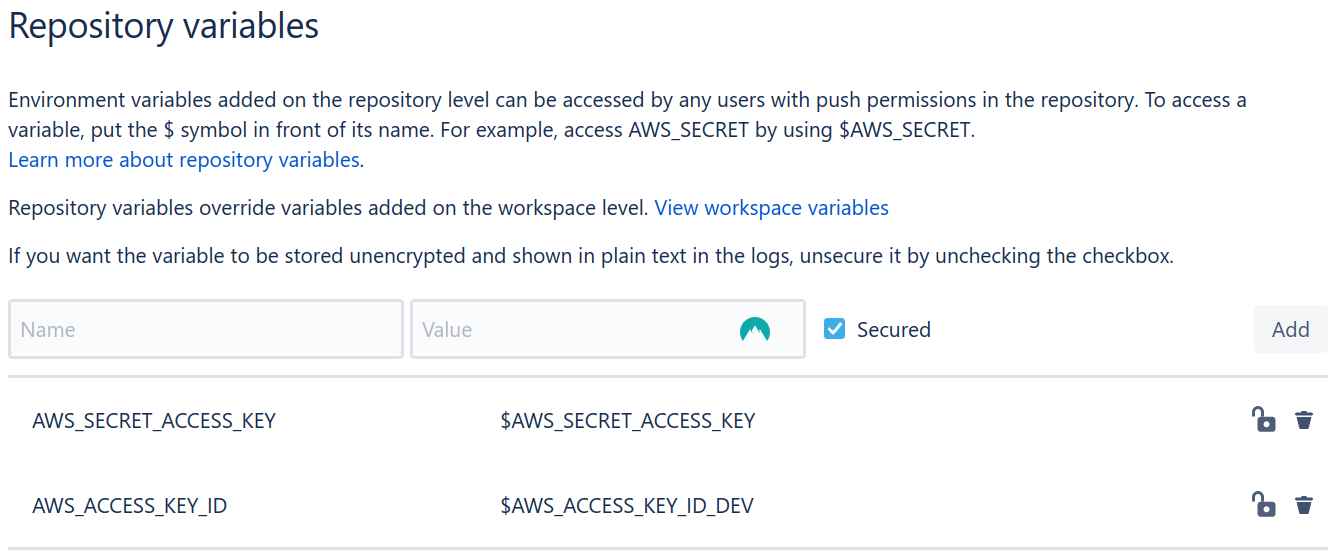
It seems that the system does not resolve the workspace level variables in the pipeline execution.
Is it possible to do this somehow?
This would allow me to define much more generic steps in bitbucket pipeline without renaming the variables in the pipeline code.
This feature would be even more beneficial to use for configuring variables for different Deployment environments without writing specific code to handle different variable names.

