Hello Atlassian community!
My name is Sandy and I'm a Cloud Trust product marketer, focused on Security. Our team is super excited to share that after a 3-month Early Access Program (EAP) with 17 enterprise customers like yourself, we are now launching multiple identity provider support as generally available in the Cloud Enterprise edition!
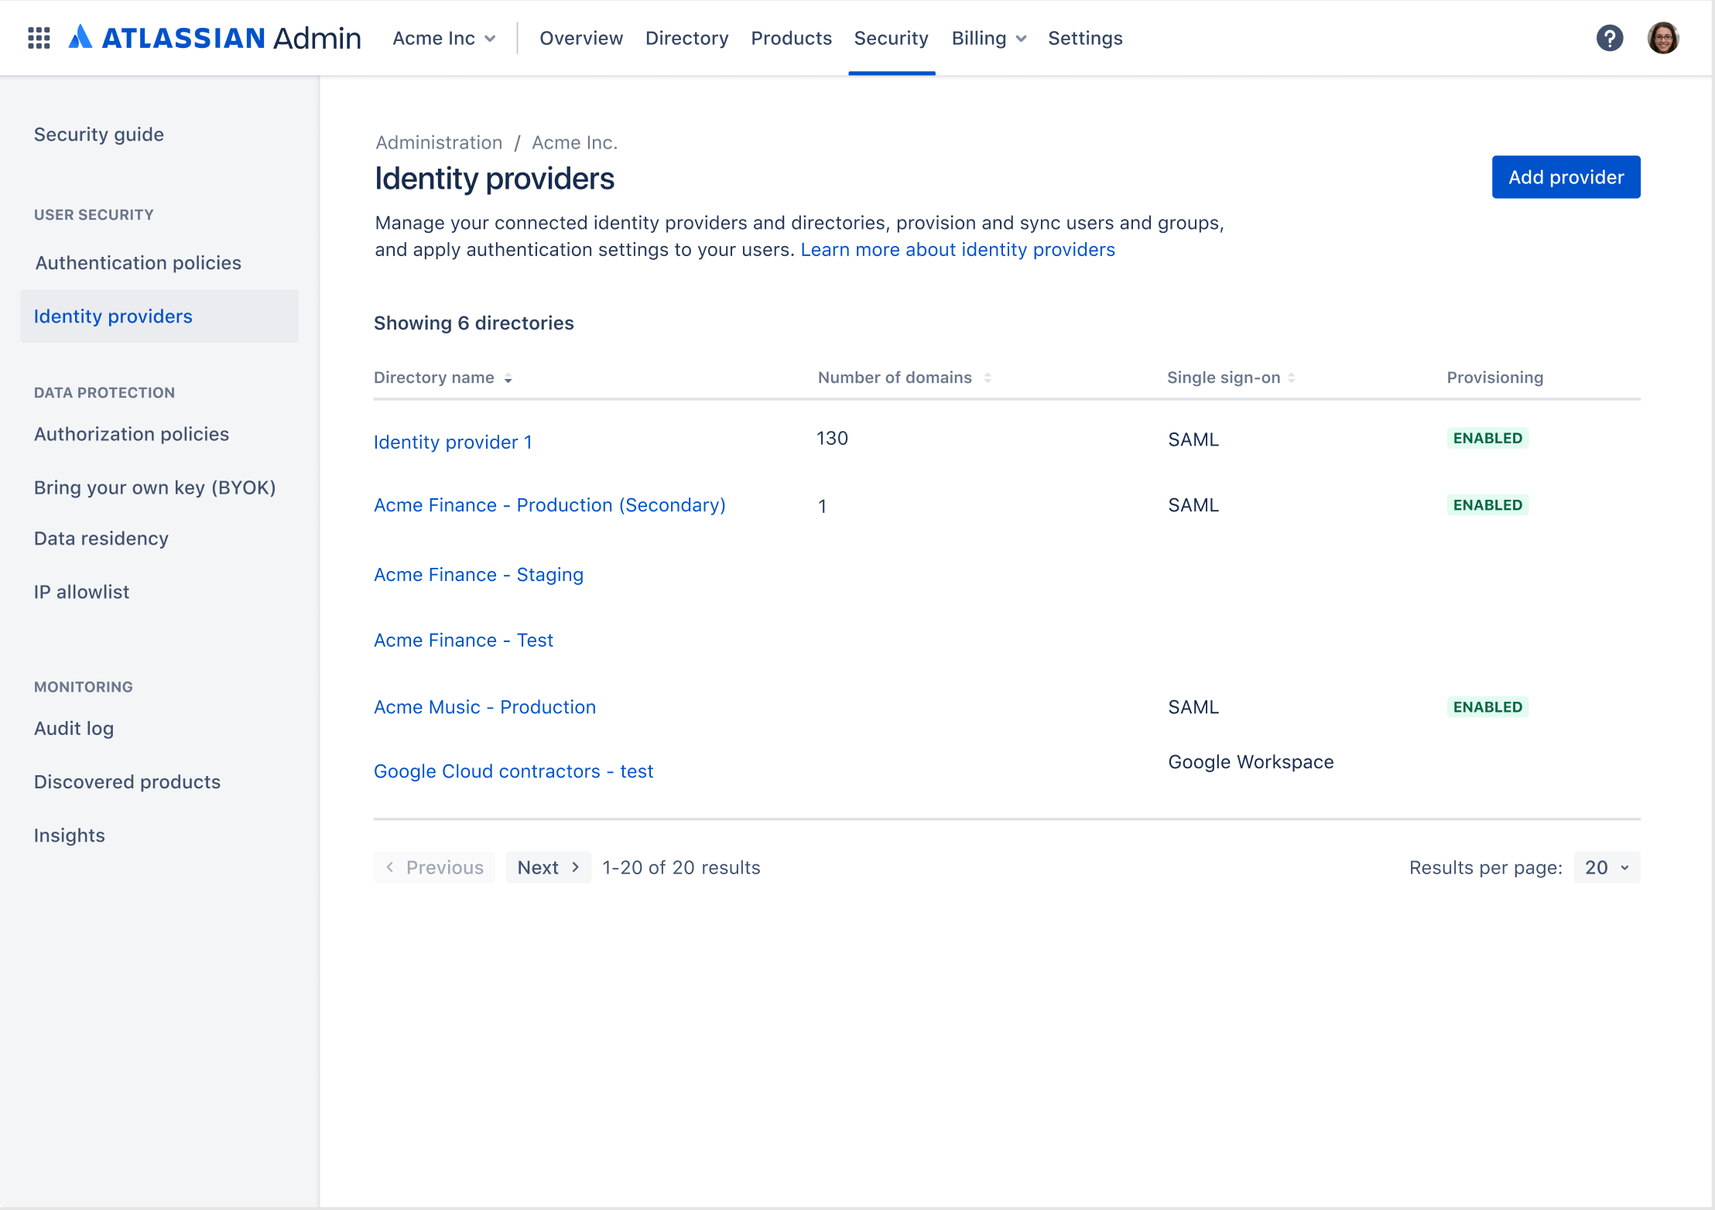
Prior to this, customers with Atlassian Access or Cloud Enterprise were only able to connect a single identity provider to implement SAML SSO and SCIM user provisioning to their Atlassian Cloud organization. Today, Cloud Enterprise customers can connect multiple identity providers, which empowers admins to:
- Quickly consolidate user management of an acquired company's identity provider within the parent company
- Maintain separate identity providers for separate departments' domains within a company
- Meet certain data residency requirements where each region needs its own identity provider
Beyond supporting multiple identity providers via the SAML/SCIM protocols, we also introduced several new capabilities to help enterprise administrators:
- Set a default authentication policy as non-billable, when not synced with an identity provider
- Connect a Google Workspace and multiple identity providers via SAML/SCIM
- Link a domain with an identity provider to manage which authentication policy new users land in
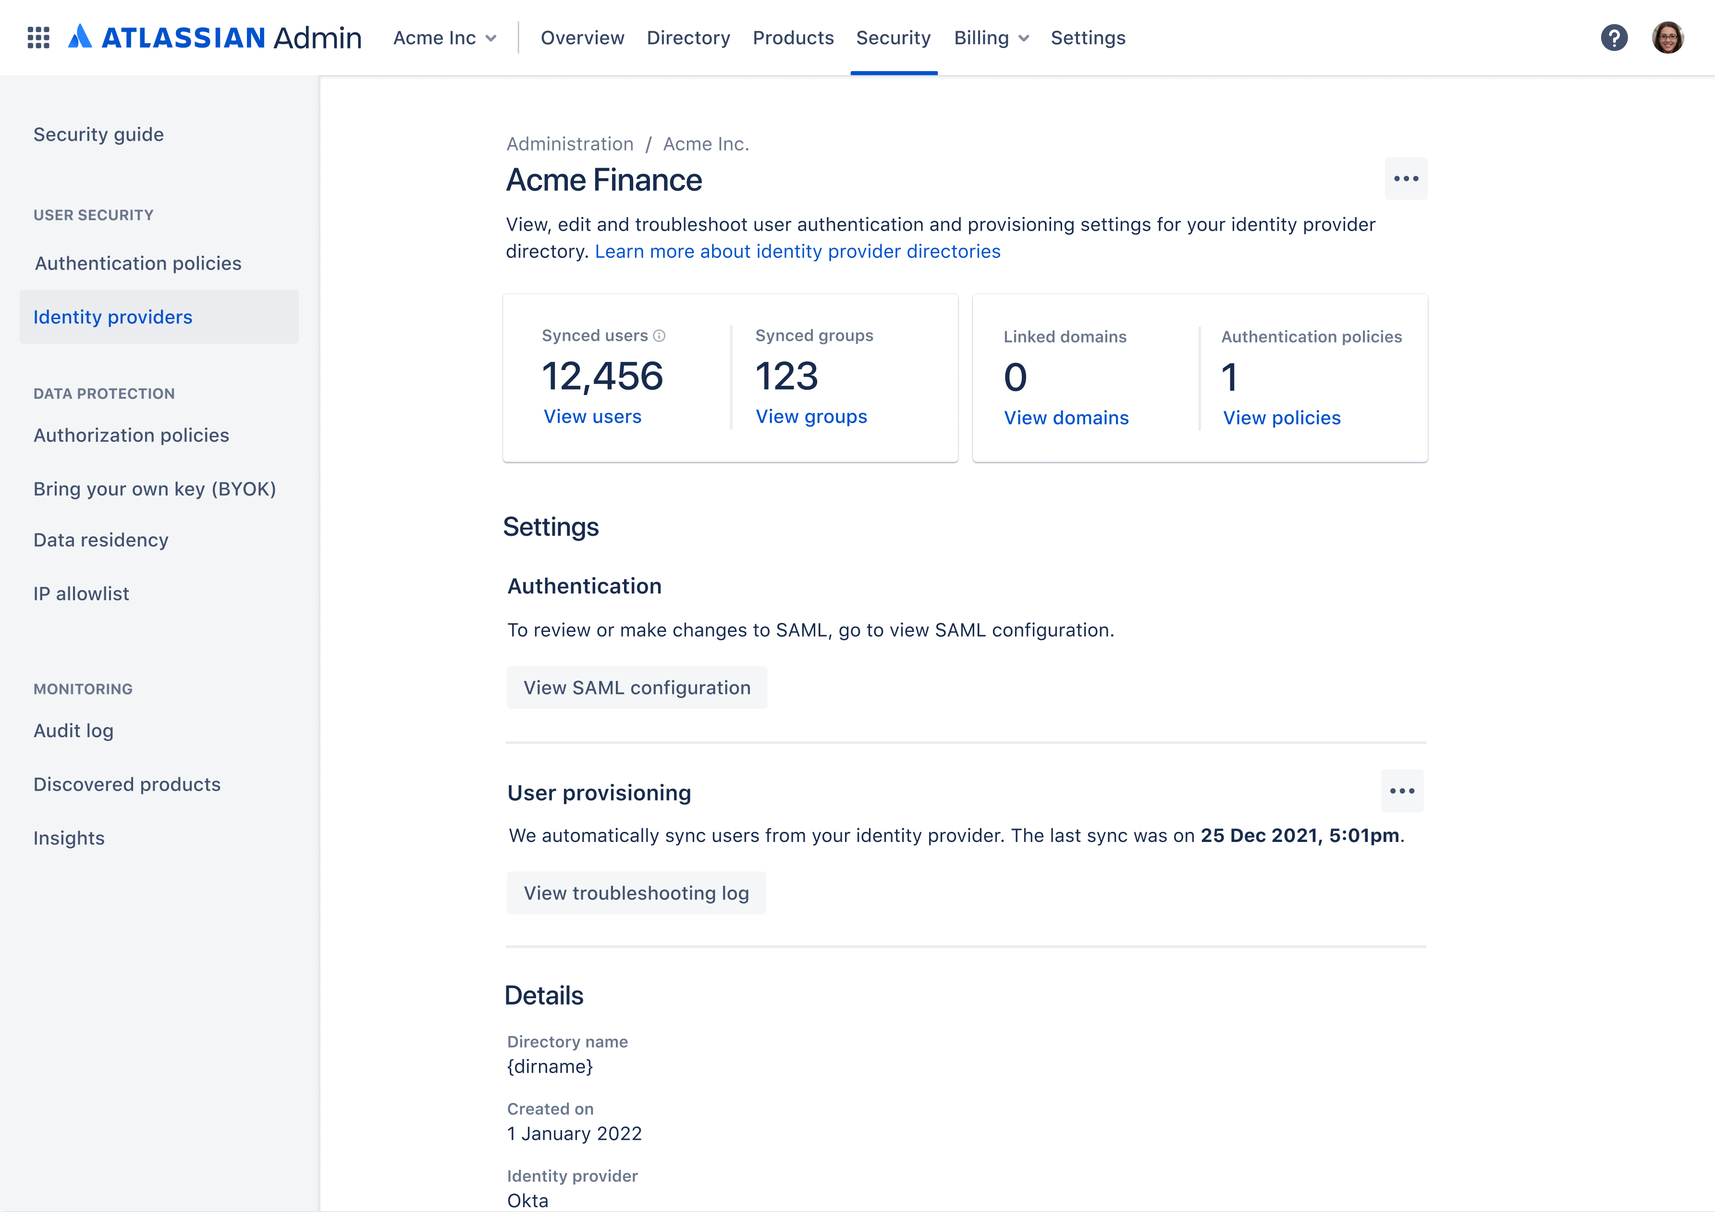
For more information about how to connect identity providers to your Atlassian Cloud organization, take a look at our documentation. If you're just getting started with your Cloud Enterprise plan, have a look at our guide here.
Are you as excited about this feature as we are? Did you find this information helpful? Please share your thoughts below – we'd love to hear from you! Be sure to take a look at other community members' comments/questions and up-vote those you find interesting.


