Dear community,
Background
We were using Jira with Tomcat over SSL and decided to move on using an NginX reverse proxy over SSL.
Previously, with Tomcat, we were redirecting all requests from 443 to 8443 as mentioned in this Confluence page.
This means that most of the users were accessing Jira using the url: https://jira.mydomain.com:8443. There are still links, within Jira (or also Confluence), that are configured with this port.
Thus, we need to be sure these links are still accessible, even behind the reverse proxy.
Nginx Configuration
We configured NginX correctly and we can access https://jira.mydomain.com without any problem, it is working like a charm
When accessing https://jira.mydomain.com:8443, we are able to login and access Jira, but the gadgets are failing to load, most likely because the Base URL is set to https://jira.mydomain.com (without the port).
See picture below when accessing https://jira.mydomain.com:8443:
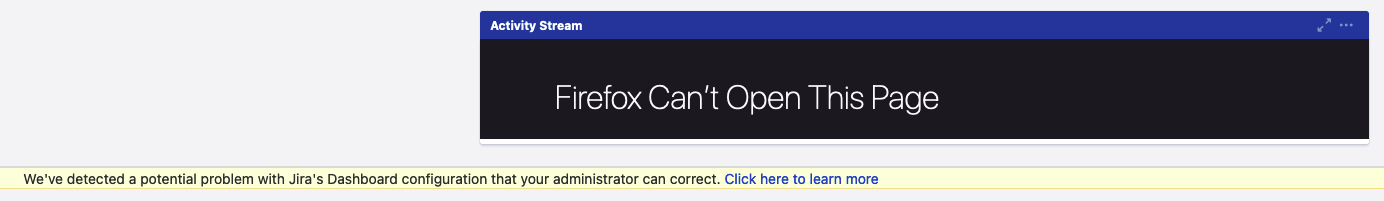
What would be the best practice and configuration to also redirect the requests with port :8443 in the URL to the appropriate proxy connector in Jira ?
nginx.conf
server {
listen 80 default_server;
listen [::]:80 default_server ipv6only=on;
server_name jira.mydomain.com;
return 301 https://$server_name$request_uri;
}

server {
listen 443 ssl http2;
listen [::]:443 ssl http2;

access_log /var/log/nginx/jira.mydomain.com.access.log main;
error_log /var/log/nginx/jira.mydomain.com.error.log;

ssl_certificate /etc/nginx/ssl/mycert.crt;
ssl_certificate_key /etc/nginx/ssl/mycert.key;
ssl_session_timeout 1d;
ssl_session_cache shared:MozSSL:10m; # about 40000 sessions
ssl_session_tickets off;

# intermediate configuration
ssl_protocols TLSv1.2 TLSv1.3;
ssl_ciphers ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:DHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384;
ssl_prefer_server_ciphers off;

# HSTS (ngx_http_headers_module is required) (63072000 seconds)
add_header Strict-Transport-Security "max-age=63072000" always;

# OCSP stapling
ssl_stapling on;
ssl_stapling_verify on;

location /secure/ForgotLoginDetails.jspa {
return 301 https://jira.mydomain.com;
}

location / {
# NGINX usually only allows 1M per request. Increase this to JIRA's maximum attachment size (10M by default)
client_max_body_size 10m;

# set proxy headers for cloudflare/jira
proxy_set_header Host $host:$server_port;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_set_header X-Forwarded-Proto $scheme;
proxy_set_header Authorization "";


# hand the request off to jira on non-ssl
proxy_pass http://localhost:8080;
}
}
server.xml
<!-- Nginx Reverse Proxy Connector -->
<Connector port="8080"
relaxedPathChars="[]|"
relaxedQueryChars="[]|{}^\`"<>"
maxThreads="150"
minSpareThreads="25"
connectionTimeout="20000"
enableLookups="false"
maxHttpHeaderSize="8192"
protocol="HTTP/1.1"
useBodyEncodingForURI="true"
redirectPort="8443"
acceptCount="100"
disableUploadTimeout="true"
bindOnInit="false"
secure="true"
scheme="https"
proxyName="jira.mydomain.com"
proxyPort="443"/>

