Hello guys,
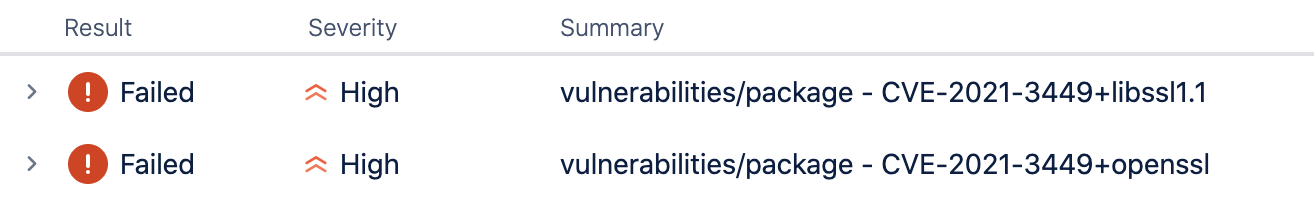
I'm currently running anchore-scan pipe (0.2.15) to scan docker images, with the default pipe policy, so is there a way to break the pipeline if the report shows vulnerabilities ?
My pipeline definition is a step with these commands :
- docker build
- anchore-scan pipe
- docker push
For example i'm running a scan to a custom docker image, it founds 2 High vulnerabilities, so i want to break the pipeline, fix the vulnerabilities a then running one again.
Thanks,

