After our linux administrator installed an SSL certificate he is currently receiving the following Tomcat config is incorrect error:
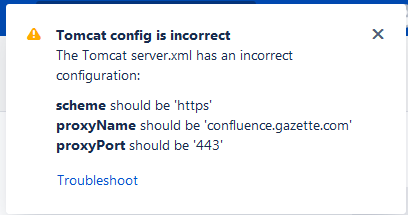
He stated he followed the troubleshooting article at https://confluence.atlassian.com/confkb/can-t-check-base-url-warning-in-confluence-6-6-or-later-939718433.html and verified the settings are correct. Most likely this is due to the article being dated. Below is the server.xml file:
<Server port="8000" shutdown="SHUTDOWN" debug="0">
<Service name="Tomcat-Standalone">
<!--
==============================================================================================================
DEFAULT - Direct connector with no proxy, for unproxied HTTP access to Confluence.
If using a http/https proxy, comment out this connector.
==============================================================================================================
-->
<!--
<Connector port="8090" connectionTimeout="20000" redirectPort="8443"
maxThreads="48" minSpareThreads="10"
enableLookups="false" acceptCount="10" debug="0" URIEncoding="UTF-8"
protocol="org.apache.coyote.http11.Http11NioProtocol"/>
-->
<!--
==============================================================================================================
HTTP - Proxying Confluence via Apache or Nginx over HTTP
If you're proxying traffic to Confluence over HTTP, uncomment the connector below and comment out the others.
Make sure you provide the right information for proxyName and proxyPort.
For more information see:
Apache - https://confluence.atlassian.com/x/4xQLM
nginx - https://confluence.atlassian.com/x/TgSvEg
==============================================================================================================
-->
<!--
<Connector port="8090" connectionTimeout="20000" redirectPort="8443"
maxThreads="48" minSpareThreads="10"
enableLookups="false" acceptCount="10" debug="0" URIEncoding="UTF-8"
protocol="org.apache.coyote.http11.Http11NioProtocol"
scheme="http" proxyName="confluence.site.com" proxyPort="80"/>
-->
<!--
==============================================================================================================
HTTPS - Direct connector with no proxy, for unproxied HTTPS access to Confluence.
For more info see https://confluence.atlassian.com/x/s3UC
==============================================================================================================
-->
<!--
<Connector port="8443" maxHttpHeaderSize="8192"
maxThreads="150" minSpareThreads="25"
protocol="org.apache.coyote.http11.Http11Nio2Protocol"
enableLookups="false" disableUploadTimeout="true"
acceptCount="100" scheme="https" secure="true"
clientAuth="false" sslProtocol="TLSv1.2" sslEnabledProtocols="TLSv1.2" SSLEnabled="true"
URIEncoding="UTF-8" keystorePass="<MY_CERTIFICATE_PASSWORD>"/>
-->
<!--
==============================================================================================================
HTTPS - Proxying Confluence via Apache or Nginx over HTTPS
If you're proxying traffic to Confluence over HTTPS, uncomment the connector below and comment out the others.
Make sure you provide the right information for proxyName and proxyPort.
For more information see:
Apache - https://confluence.atlassian.com/x/PTT3MQ
nginx - https://confluence.atlassian.com/x/cNIvMw
==============================================================================================================
-->
<Connector port="8090" connectionTimeout="20000" redirectPort="8443"
maxThreads="48" minSpareThreads="10"
enableLookups="false" acceptCount="10" debug="0" URIEncoding="UTF-8"
protocol="org.apache.coyote.http11.Http11NioProtocol"
scheme="https" secure="true" proxyName="confluence.site.com" proxyPort="443"/>
<Engine name="Standalone" defaultHost="localhost" debug="0">
<Host name="localhost" debug="0" appBase="webapps" unpackWARs="true" autoDeploy="false" startStopThreads="4">
<Context path="" docBase="../confluence" debug="0" reloadable="false" useHttpOnly="true">
<!-- Logging configuration for Confluence is specified in confluence/WEB-INF/classes/log4j.properties -->
<Manager pathname=""/>
<Valve className="org.apache.catalina.valves.StuckThreadDetectionValve" threshold="60"/>
</Context>
<Context path="${confluence.context.path}/synchrony-proxy" docBase="../synchrony-proxy" debug="0"
reloadable="false" useHttpOnly="true">
<Valve className="org.apache.catalina.valves.StuckThreadDetectionValve" threshold="60"/>
</Context>
</Host>
</Engine>
</Service>
</Server>
Also, here is the nginx.conf file:
server {
listen confluence.site.com:80;
server_name confluence.site.com;
listen 443 default ssl;
ssl_certificate /etc/ssl/private/confluence.site.com.crt;
ssl_certificate_key /etc/ssl/private/confluence.site.com.key;
ssl_session_timeout 5m;
ssl_protocols TLSv1 TLSv1.1 TLSv1.2;
ssl_ciphers 'ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-AES128-SHA256:ECDHE-RSA-AES128-SHA256:ECDHE-ECDSA-AES128-SHA:ECDHE-RSA-AES256-SHA384:ECDHE-RSA-AES128-SHA:ECDHE-ECDSA-AES256-SHA384:ECDHE-ECDSA-AES256-SHA:ECDHE-RSA-AES256-SHA:ECDHE-ECDSA-DES-CBC3-SHA:ECDHE-RSA-DES-CBC3-SHA:EDH-RSA-DES-CBC3-SHA:AES128-GCM-SHA256:AES256-GCM-SHA384:AES128-SHA256:AES256-SHA256:AES128-SHA:AES256-SHA:DES-CBC3-SHA:!DSS';
ssl_prefer_server_ciphers on;
location / {
client_max_body_size 100m;
proxy_set_header X-Forwarded-Host $host;
proxy_set_header X-Forwarded-Server $host;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_pass http://localhost:8090;
}
location /synchrony {
proxy_set_header X-Forwarded-Host $host;
proxy_set_header X-Forwarded-Server $host;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_pass http://localhost:8091/synchrony;
proxy_http_version 1.1;
proxy_set_header Upgrade $http_upgrade;
proxy_set_header Connection "Upgrade";
}
}

