Hey everyone, I'm Lee, a Product Manager in the Security department here at Atlassian. I wanted to let you know that we've made a few updates to the format of our security bulletins as a first step to address the heightened volume of support tickets and questions ("Is my version affected?") that we regularly receive regarding our security bulletins. I'm also here to let you know that we are actively seeking feedback from the community for these bulletin updates and the various security resources Atlassian provides.
First, let's review the notable updates this month's Security Bulletin:
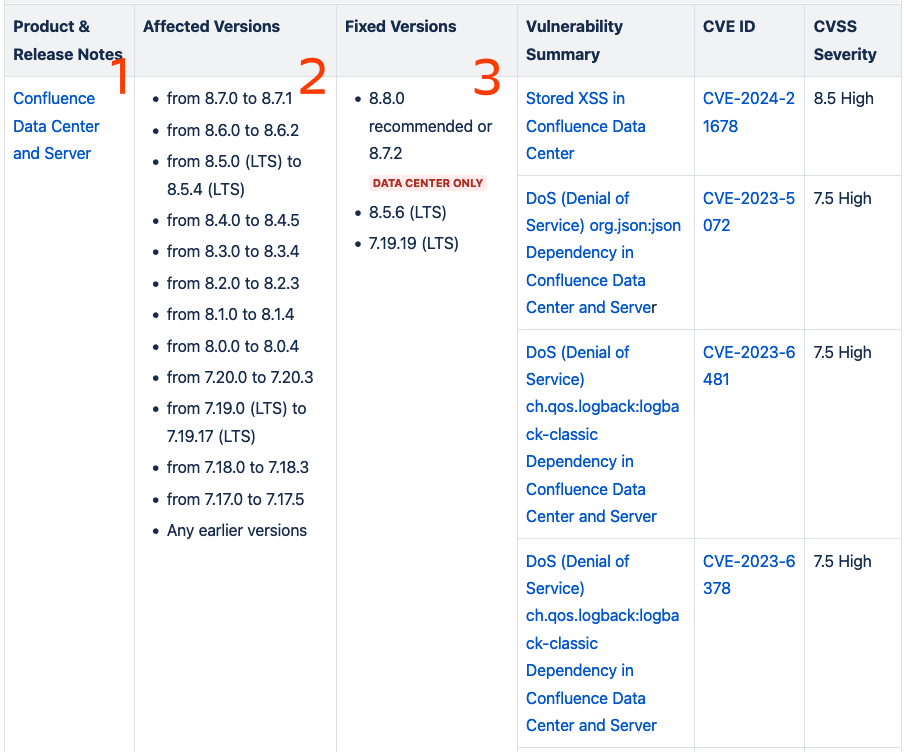
- Grouped By Product - The new bulletin table is organized by product, allowing you to locate information relevant to the Atlassian Product(s) you are using as quickly as possible.
- Full Range of Affected Versions We have included a complete list of affected product versions, being sure to include all product versions listed as supported according to our Atlassian Support End of Life Policy Page. While this is quite verbose, our primary goal is answer the "Am I affected" question.
- Comprehensive Fixed Versions The table shows each product's fixed versions for all the security vulnerabilities that affected the product in that particular bulletin. Patching to one of these versions will resolve all the vulnerabilities listed for the product in the bulletin.
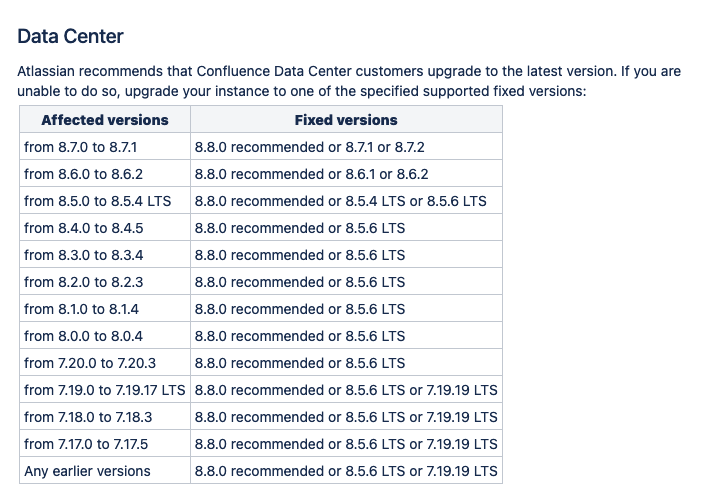
- Additional Jira Ticket Details For the published Public Security Vulnerability tickets on Jira.Atlassian.com, as part of this bulletin, we have published a detailed Affected & Fixed Version table specific to the individual vulnerability. When referencing details via these Security Jira tickets - This table can answer questions regarding whether your version is affected for the Product and CVE specified on the ticket by finding your version in the "Affected versions" column and then checking the associated "Fixed versions" in the right column.
We believe these enhancements will make it easier to quickly identify the impact of vulnerabilities and take appropriate action to secure your systems without needing to file a support ticket to answer your security bulletin-related questions.
We look to take an iterative approach based on feedback to improve our bulletins, advisories, and the various security resources Atlassian provides. I would appreciate any feedback you might have for us, feel free to reach out! Thank you, I'm looking forward to working with this community!


