Hello,
I would like to use the LDAPS connector to my active directory. Since I have multiple active directory servers, I need to use a loadbalancer IP within the LDAPS connection string.
Now obiously, this IP does not match the certificate installed on the active directory server. The active directory root ca certificates are yet installed on the crowd server.
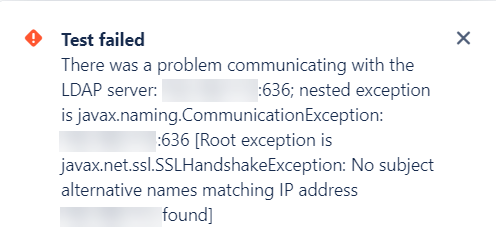
Unfortunately, I can not add any SAN IPs to the certificate as the CA does not support this.
Is there any way to enable LDAPS without certificate checking?
Best regards,
Jan

