While using source tree with embedded git or system git, user stores their credentials in the preferences of source tree or in keychain/credential manager depending on the OS. Now when their cloud credential gets changed and if they forget to change the local stored credentials, Source tree sends multiple request to bitbucket without prompting the user to enter correct credentials after the first failure which gets their user account locked from the corporate system to avoid brute force attack.
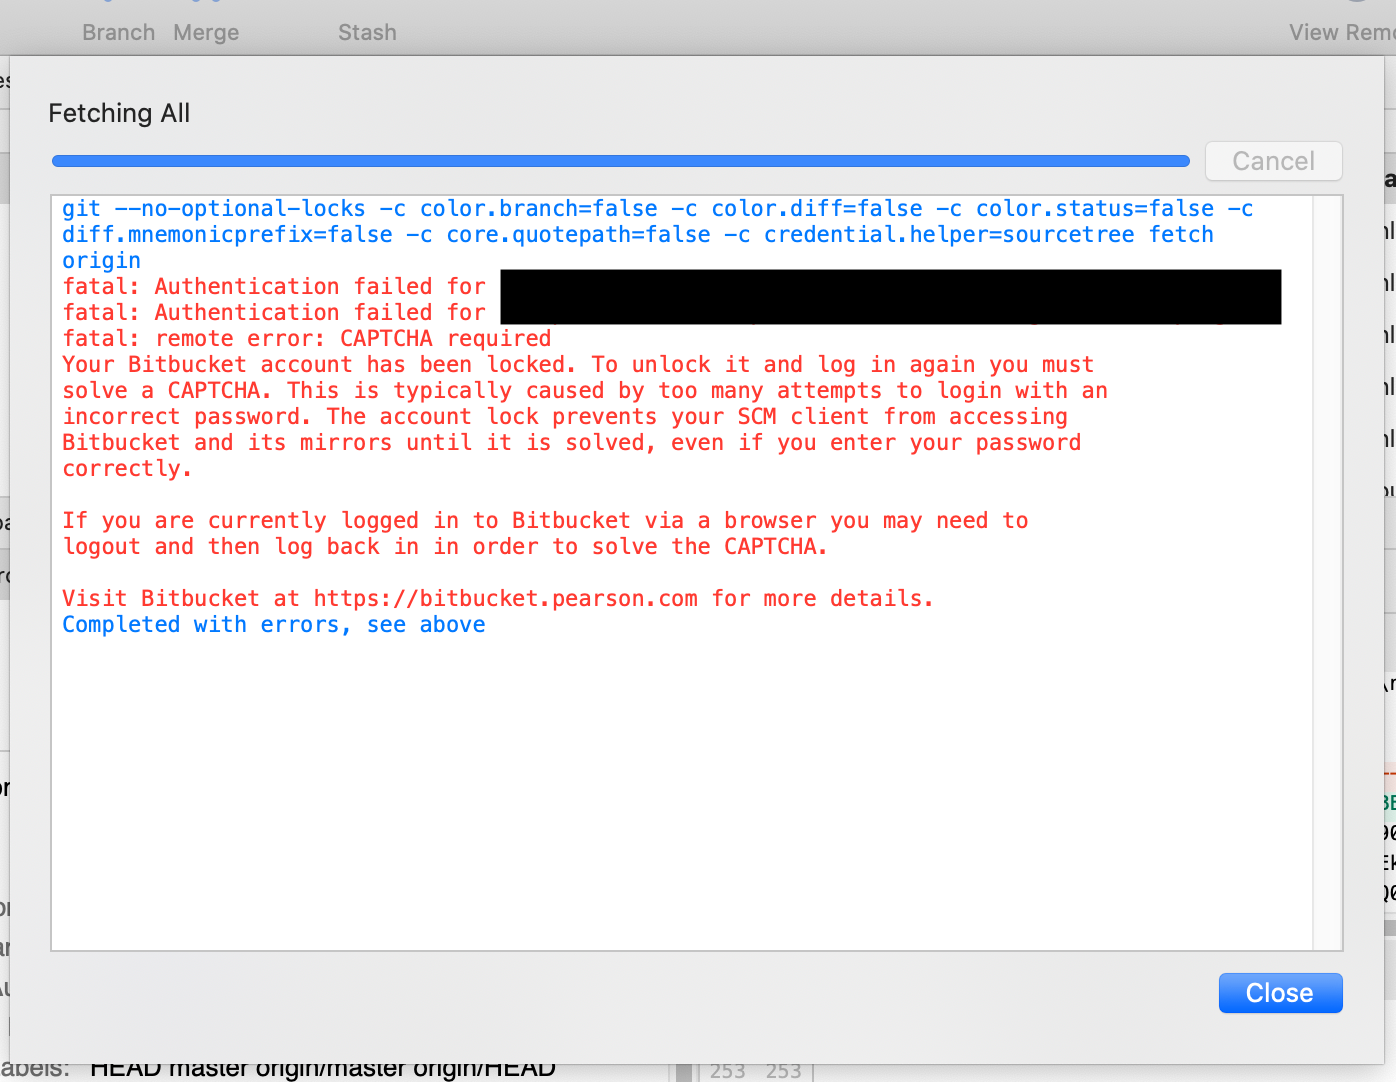
Due to above mentioned reason our company's IT Team is denying the access to use source tree and source tree application has been blacklisted in our company.
Following is the explanation I received from our company's IT Security team for blacklisting source tree application and not allowing company developers to use source tree:
"Good applications should tell you that you entered the incorrect password. SourceTree does not, and silently retries without notification to the user until the lockout occurs (and even then, I am not sure it tells you your account is locked out, it just keeps trying the bad password, so it would continue to cause lockouts). That is a denial of service vulnerability."
Expected Resolution from IT Team:
Source tree should only send one request to bitbucket ui to confirm if the credentials are valid and if credential are invalid then prompt user to enter correct credentials or as them to change their local cached credentials before sending another request to bitbucket.
Can I request Atlassian to look into this issue.


