Hello,
I’d like to know if anyone was able to integrate OpsGenie with the last version of Splunk (7.2.*).
We use Splunk 7.2.5 and Splunk Enterprise Security 5.2.2 and we’d like to automatically create an alert in OpsGenie whenever an alert is created in Splunk.
We've installed OpsGenie Splunk app, but it looks pretty obsolete (last version published Oct. 31, 2017) and doesn’t seem to work correctly:
- In Splunk you can add OpsGenie as a response action, but you can’t manage any detail, like alert priority, etc.
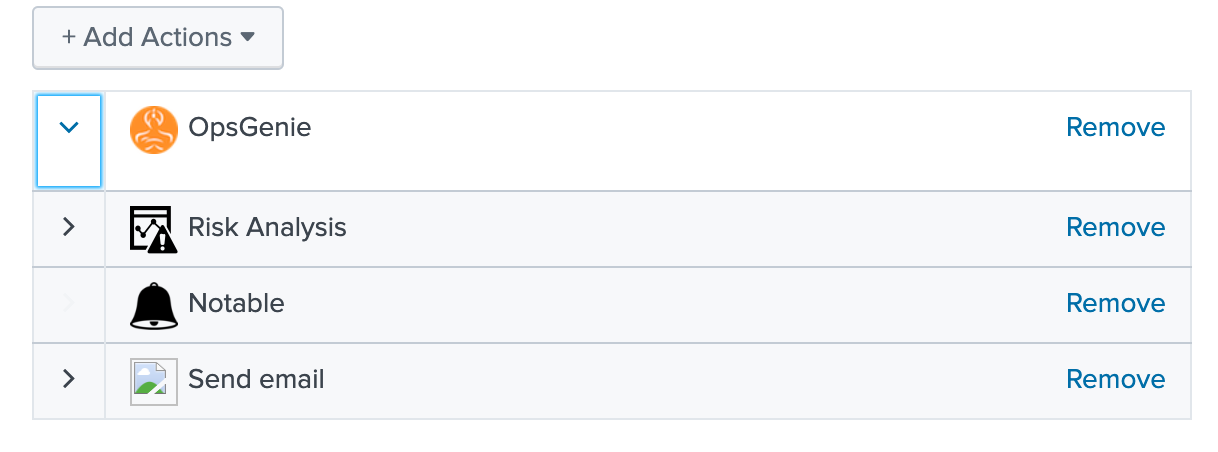
- In Splunk Enterprise Security there is no OpsGenie action in the response action list at all.
Do you have any advice for us?
Thanks for the help.
Alex.


